Tagged: RFID

Thermal Noise Communication: Sending Data Without a Carrier Signal, with an RTL-SDR as the Receiver

Thank you to RTL-SDR.COM reader Andrea for writing in and pointing us to a recent Stanford University press release about Zerina Kapetanovic and her team's research on "thermal noise communication", a way to send data wirelessly without generating any RF signal at all.

With this communication method, the transmitter simply switches its antenna between two loads, such as a dummy load and an open circuit, which the receiver sees as slightly "hotter" or "colder" thermal noise that encodes binary data. The study claims that a conventional RF transmitter uses up to 1,000 times more energy, making this a possible alternative to RFID tags and low-power wireless sensors.

Our reader Andrea also pointed out that the receiver in one of Zerina Kapetanovic's earlier experiments on the same topic was built around an RTL-SDR. Back in 2022, Zerina Kapetanovic and her team published a paper (pdf upload) demonstrating the idea at 1.42 GHz. Their receiver was a horn antenna, two LNAs with about 84 dB of combined gain, a bandpass filter, and an RTL-SDR, with processing on a laptop or Raspberry Pi. The transmitter was a simple RF switch connected to an antenna and switched between a 50 Ohm dummy load or ground. They achieved a data rate of up to 26 bps and a range of up to 7.3 m at 5 bps, and built a solar-powered, battery-free transmitter that sent indoor temperature readings over five days.

A new paper (not available freely yet) from Kapetanovic and her team builds on this idea and improves the data rate to the kilobit-per-second range, and adds capacity measurements and error correction, which was a limitation of their earlier experiment. The paper and press release also explain why this idea works at room temperature, making the analogy that the receiver's LNA works as a sort of 'electron refrigerator', slowing down electrons and making them appear colder.

We are unsure if the new setup still uses an RTL-SDR. However, readers who have built a Hydrogen line radio telescope have already built a nearly identical setup to the 2022 paper. In the press release Kapetanovic notes that "We've built a system that others could very easily implement", so this may be an interesting experiment to try for anyone who already has an H-line setup.
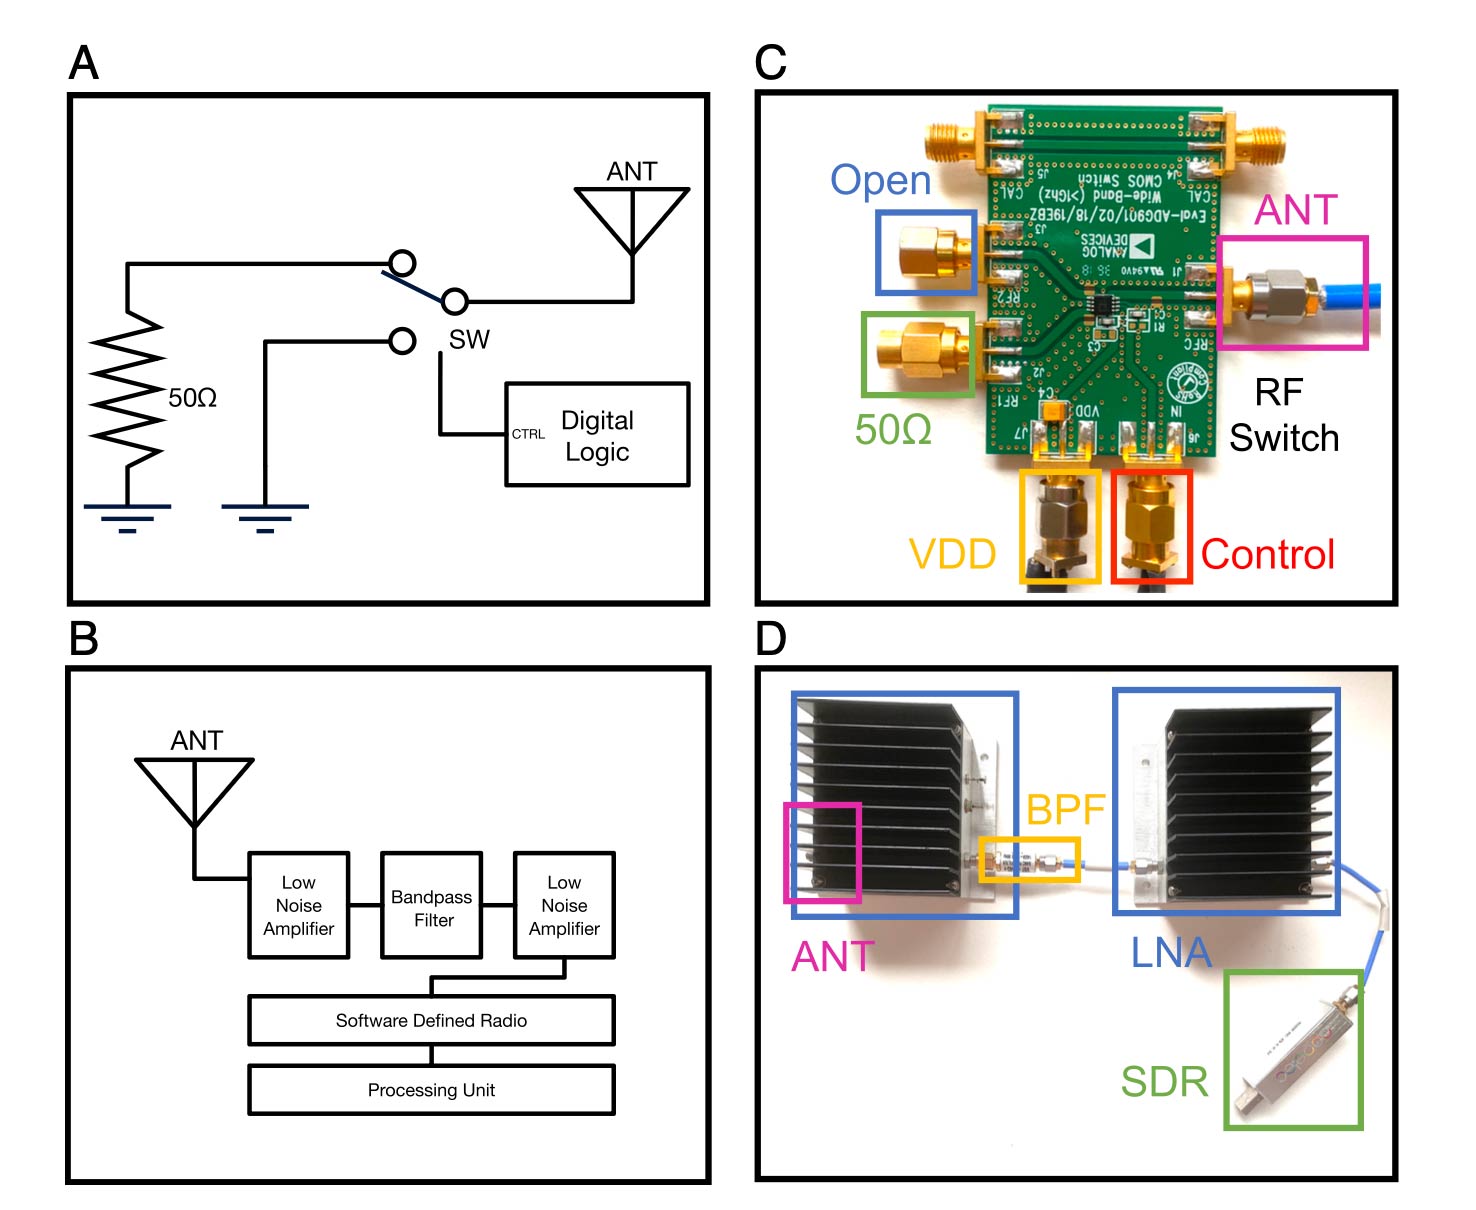
The thermal noise receiver setup from the 2022 paper

Upcoming Book “Inside Radio: An Attack and Defense Guide”

Unicorn team are information security researchers who often also dabble with wireless security research. Recently they have been promoting their upcoming text book titled "Inside Radio: An Attack and Defense Guide".

Judging from the blurb and released contents the book will be an excellent introduction to anyone interested in today's wireless security issues. They cover topics such as RFID, Bluetooh, ZigBee, GSM, LTE and GPS. In regards to SDRs, the book specifically covers SDRs like the RTL-SDR, HackRF, bladeRF and LimeSDR and their role in wireless security research. They also probably reference and show how to use those SDRs in the  chapters about replay attacks, ADS-B security risks, and GSM security.

The book is yet to be released and is currently available for pre-order on Amazon or Springer for US$59.99. The expected release date is May 9, 2018, and copies will also be for sale at the HITB SECCONF 2018 conference during 9 - 13 April in Amsterdam.

The blurb and released contents are pasted below. See their promo page for the full contents list:

This book discusses the security issues in a wide range of wireless devices and systems, such as RFID, Bluetooth, ZigBee, GSM, LTE, and GPS. It collects the findings of recent research by the UnicornTeam at 360 Technology, and reviews the state-of-the-art literature on wireless security. The book also offers detailed case studies and theoretical treatments – specifically it lists numerous laboratory procedures, results, plots, commands and screenshots from real-world experiments. It is a valuable reference guide for practitioners and researchers who want to learn more about the advanced research findings and use the off-the-shelf tools to explore the wireless world.

Authors:
Qing YANG is the founder of UnicornTeam & the head of the Radio Security Research Department at 360 Technology. He has vast experience in information security area. He has presented at Black Hat, DEFCON, CanSecWest, HITB, Ruxcon, POC, XCon, China ISC etc.

Lin HUANG is a senior wireless security researcher and SDR technology expert at 360 Technology. Her interests include security issues in wireless communication, especially cellular network security. She was a speaker at Black Hat, DEFCON, and HITB security conferences. She is 360 Technology’s 3GPP SA3 delegate.

This book is a joint effort by the entire UnicornTeam, including Qiren GU, Jun LI, Haoqi SHAN, Yingtao ZENG, and Wanqiao ZHANG etc.


EM-ID: RTL-SDR based Tag-Less ID of Electrical Devices via Eletromagnetic Emissions

Back in November 2015 we posted about Disney Research’s EM-Sense which was an RTL-SDR based smart watch that was able to actually sense and detect the exact (electronic) object the wearer was touching. It worked by using the RTL-SDR to detect the specific electromagnetic emission signature given off by various different electronic devices.

Now Disney research has just released a new paper titled “EM-ID: Tag-less Identification of Electrical Devices via Electromagnetic Emissions”. In this paper the authors describe an RTL-SDR based system which serves as a replacement for RFID tags and readers. RFID (Radio Frequency ID) tags can be used in place of standard barcodes when placed on items as a means for easy inventory and asset tracking. An RFID tag is faster and easier to read than a barcode, but the individual cost of the tag has prevented its widespread adoption.

The Disney research team have put forward the idea that a low cost SDR like the RTL-SDR can be used in place of RFID tags when they would have been used to identify electronic devices. The idea is that the SDR can be used to read the electromagnetic emissions of the electronic device, which can then be used to identify the item, thus eliminating the need for an RFID tag or barcode. Their abstract reads:

Radio Frequency Identification technology has greatly improved asset management and inventory tracking. However, for many applications RFID tags are considered too expensive compared to the alternative of a printed bar code, which has hampered widespread adoption of RFID technology. 

To overcome this price barrier, our work leverages the unique electromagnetic emissions generated by nearly all electronic and electromechanical devices as a means to individually identify them. This tag-less method of radio frequency identification leverages previous work showing that it is possible to classify objects by type (i.e. phone vs. TV vs. kitchen appliance, etc). A core question is whether or not the electromagnetic emissions from a given model of device, is sufficiently unique to robustly distinguish it from its peers. 

We present a low cost method for extracting the EM-ID from a device along with a new classification and ranking algorithm that is capable of identifying minute differences in the EM signatures. Results show that devices as divers as electronic toys, cellphones and laptops can all be individually identified with an accuracy between 72% and 100% depending on device type.

While not all electronics are unique enough for individual identifying, we present a probability estimation model that accurately predicts the performance of identifying a given device out of a population of both similar and dissimilar devices. Ultimately, EM-ID provides a zero cost method of uniquely identifying, potentially billions of electronic devices using their unique electromagnetic emissions.

An EM-ID use case: Identifying difference laptop assets.

In the paper we can see that the EM-ID hardware is essentially just a direct sampling modified RTL-SDR and antenna. The RTL-SDR is modified to use direct sampling as this allows it to receive 0 – 28 MHz, and thus 0 – 500 kHz where the most useful EM emissions exist. The system process is to basically scan the device using the antenna and RTL-SDR, extract features such as power peaks from the recorded EMI spectrum and then turn this data into a device signature which can then be used to compare against a database of previously recorded and known device signatures. (e.g. light bulb, iPhone).

The EM-ID Hardware: Essentially an RTL-SDR and antenna.
The EM-ID Process.
The EM-ID Process.

Analyzing a Car Security Active RFID Token with a HackRF

Some car security systems from around 2001 – 2003 use an embedded RFID tag inside the car key as an added security measure against key copying. Using his HackRF, ChiefTinker was able to analyse and decode the data from an active RFID token used in a car key. He notes that the same analysis could also be performed with an RTL-SDR dongle.

Upon powering the RFID tag with a power supply, ChiefTinker noticed that the tag emitted a short transmission every 5 seconds in the ISM band at 433.920 MHz. On closer inspection he determined that the transmitted data was encoded with a simple AM on-off keying (OOK) scheme. After importing the audio into Audacity and cleaning up the signal a little, he was able to clearly see the OOK square wave showing the transmitted binary data.

Next he analysed the data and compared the binary output against two different RFID keys. From the comparison he was able to determine that the tag simply beacons a unique serial number, which is susceptible to capture and replay attacks. After further processing he was able to convert the transmitted binary serial number into hexadecimal, then ASCII to find the unique serial number being broadcast in decimal.

RFID Car Key Tokens
RFID Car Key Tokens