Tagged: tempest

SPECTER: Leaking Data from Air-Gapped Computers by Toggling USB Power States

This October, researchers Hyeongjun Choi, Ji Hyuk Jung and Ji Won Yoon from Korea University and 78ResearchLab in Seoul have published a paper describing "SPECTER", a covert channel that leaks data from air-gapped computers by repeatedly switching the power state of attached USB devices. This first requires installing malware with root or administrator privileges, which then controls power via the operating system's suspend or disable/enable controls. No modification to the peripheral's hardware or firmware is needed.

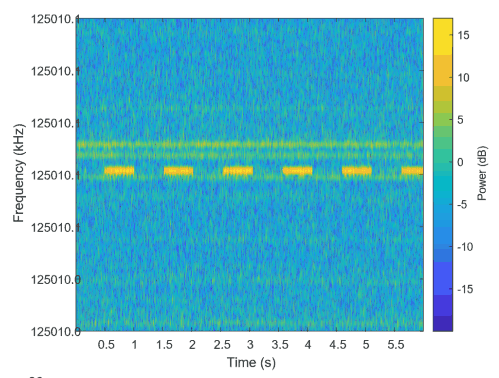
Three receiving methods were demonstrated, with one being RF based. The first method uses a phone plugged into the port, which then simply logs its charging state as on/off binary data. The second method uses a connected mouse, webcam or USB hub whose status LEDs can be watched by a person or camera. The final method uses a HackRF One with a near-field loop probe to pick up the switching emissions at around 5 MHz. Data rates are only 0.2 to 1 bit per second, so the channel is only useful for short secrets like passwords or keys.

We note that so far, the RF method was only tested with the probe touching the USB cable. This project is similar to USBee, which we posted about in 2016, where an unmodified USB device was also turned into a transmitter via malware. The difference is that USBee requires a data transfer USB device like a thumb drive to be connected, whereas SPECTER can use any connected USB device, even those that are charge-only.
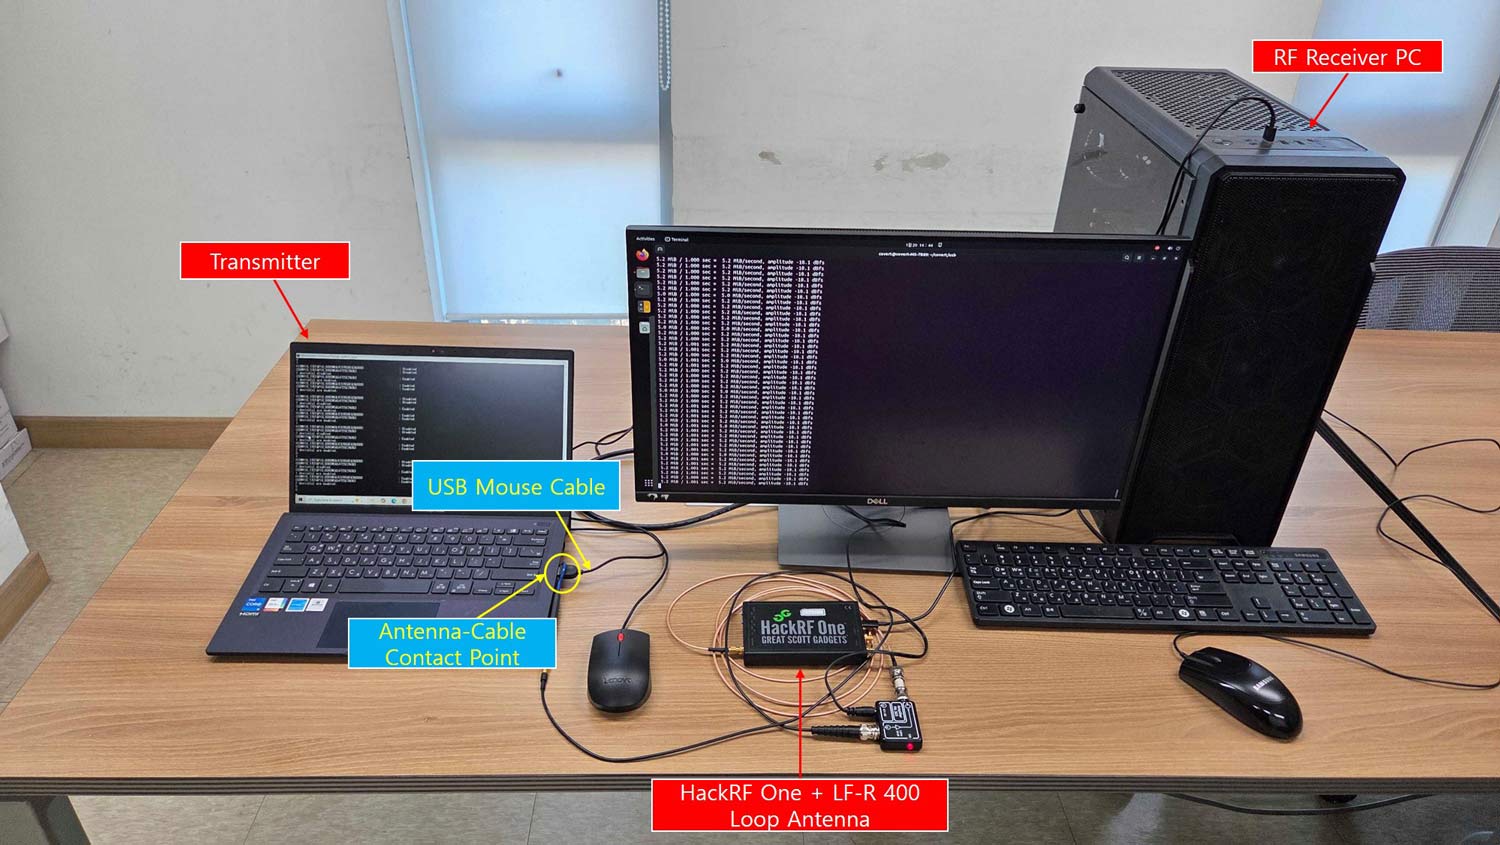
SPECTER RF Receiver Setup with a HackRF One and Loop Probe

InjectEave: Eavesdropping on Headphones by Injecting a Carrier and Listening to the Modulated Retransmission

Researchers from the Hong Kong University of Science and Technology (Guangzhou) and the Hong Kong Polytechnic University recently published a paper titled "Injected and Leaked: Actively Inducing Side-Channel Leakage Using Electromagnetic Injection and Hardware Nonlinearity".

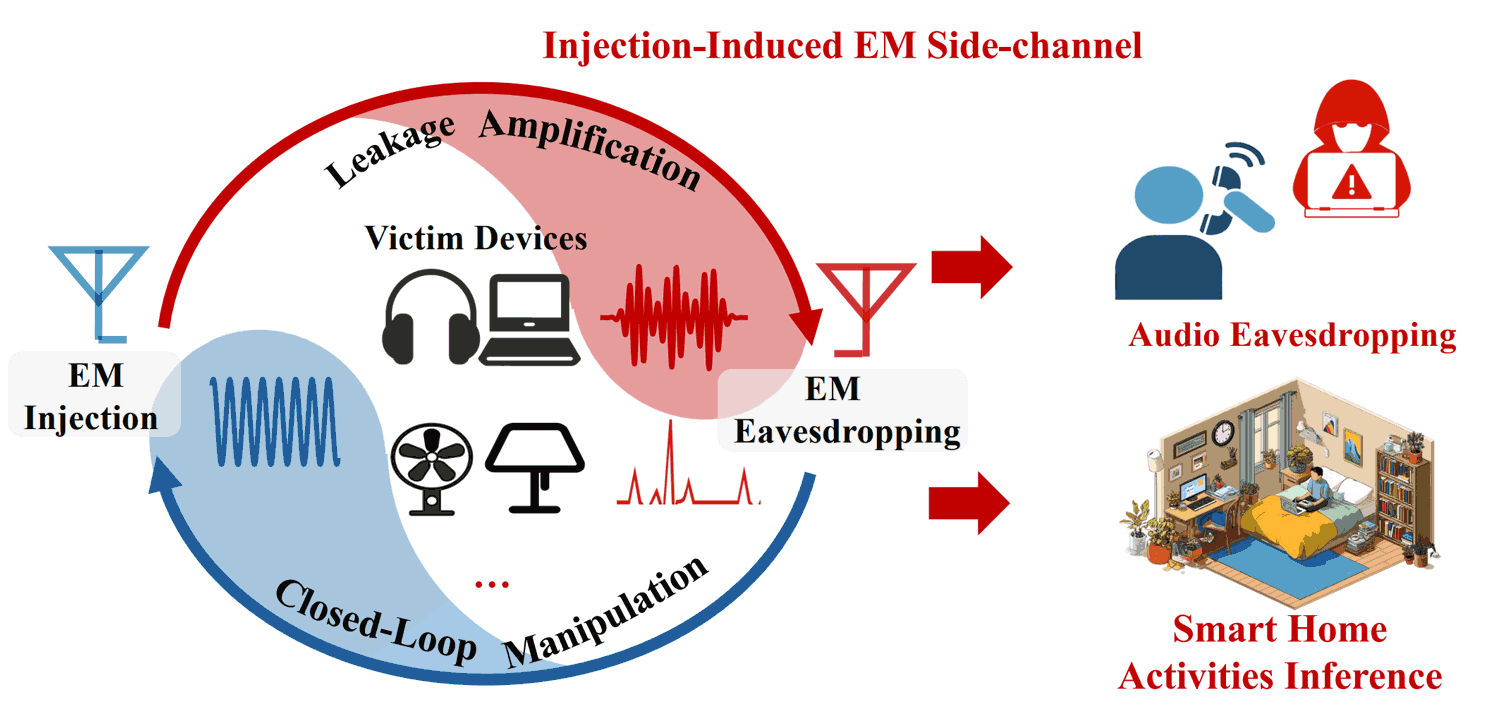
The paper describes how an attacker can use a directional antenna to transmit a carrier signal toward an electronic device, where nonlinearities in its components modulate the signal, which connected cables then re-radiate as unintentional antennas. The attacker can then receive the modulated carrier at the same frequency as it is transmitted and demodulate the modulated sidebands.

The Injecteave Process

In their experiments, they used a USRP B210 software-defined radio to transmit the CW injection signal at anywhere from 0 to 8 MHz (the exact frequency for a device is not specified in the paper for ethical considerations), and a spectrum analyzer to receive the injection-induced EM leakage. The spectrum analyzer demodulates the received mixed signal, then routes the baseband to a PC for further processing. They show how various wired and wireless headphones exhibited injection-induced leakage via the amplifier, and how landline desk phones, smart fans, and lamps were also susceptible.

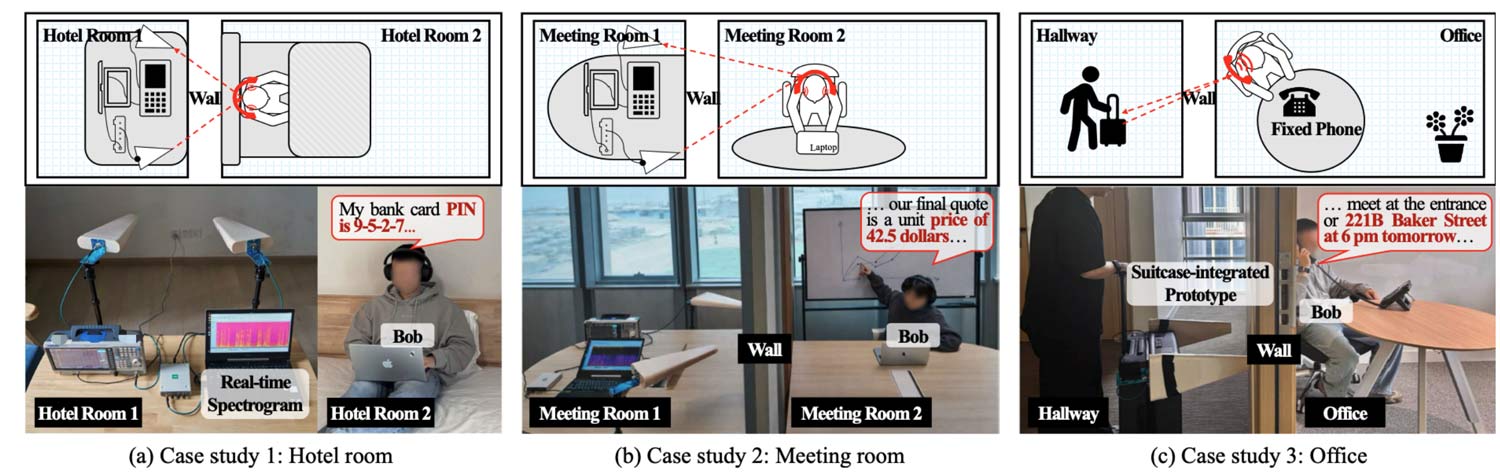
They also show a real-world application where they eavesdropped on audio from headphones and desk phones through walls in a hotel, meeting room, and office.

Update: Thanks to a commenter for pointing out the InjectEave demo page at https://injecteave.github.io.

InjectEave: Real World Examples

An HTML Browser Page that Uses Display Pixel Clock EMI Leakage to Transmit VHF Morse Code

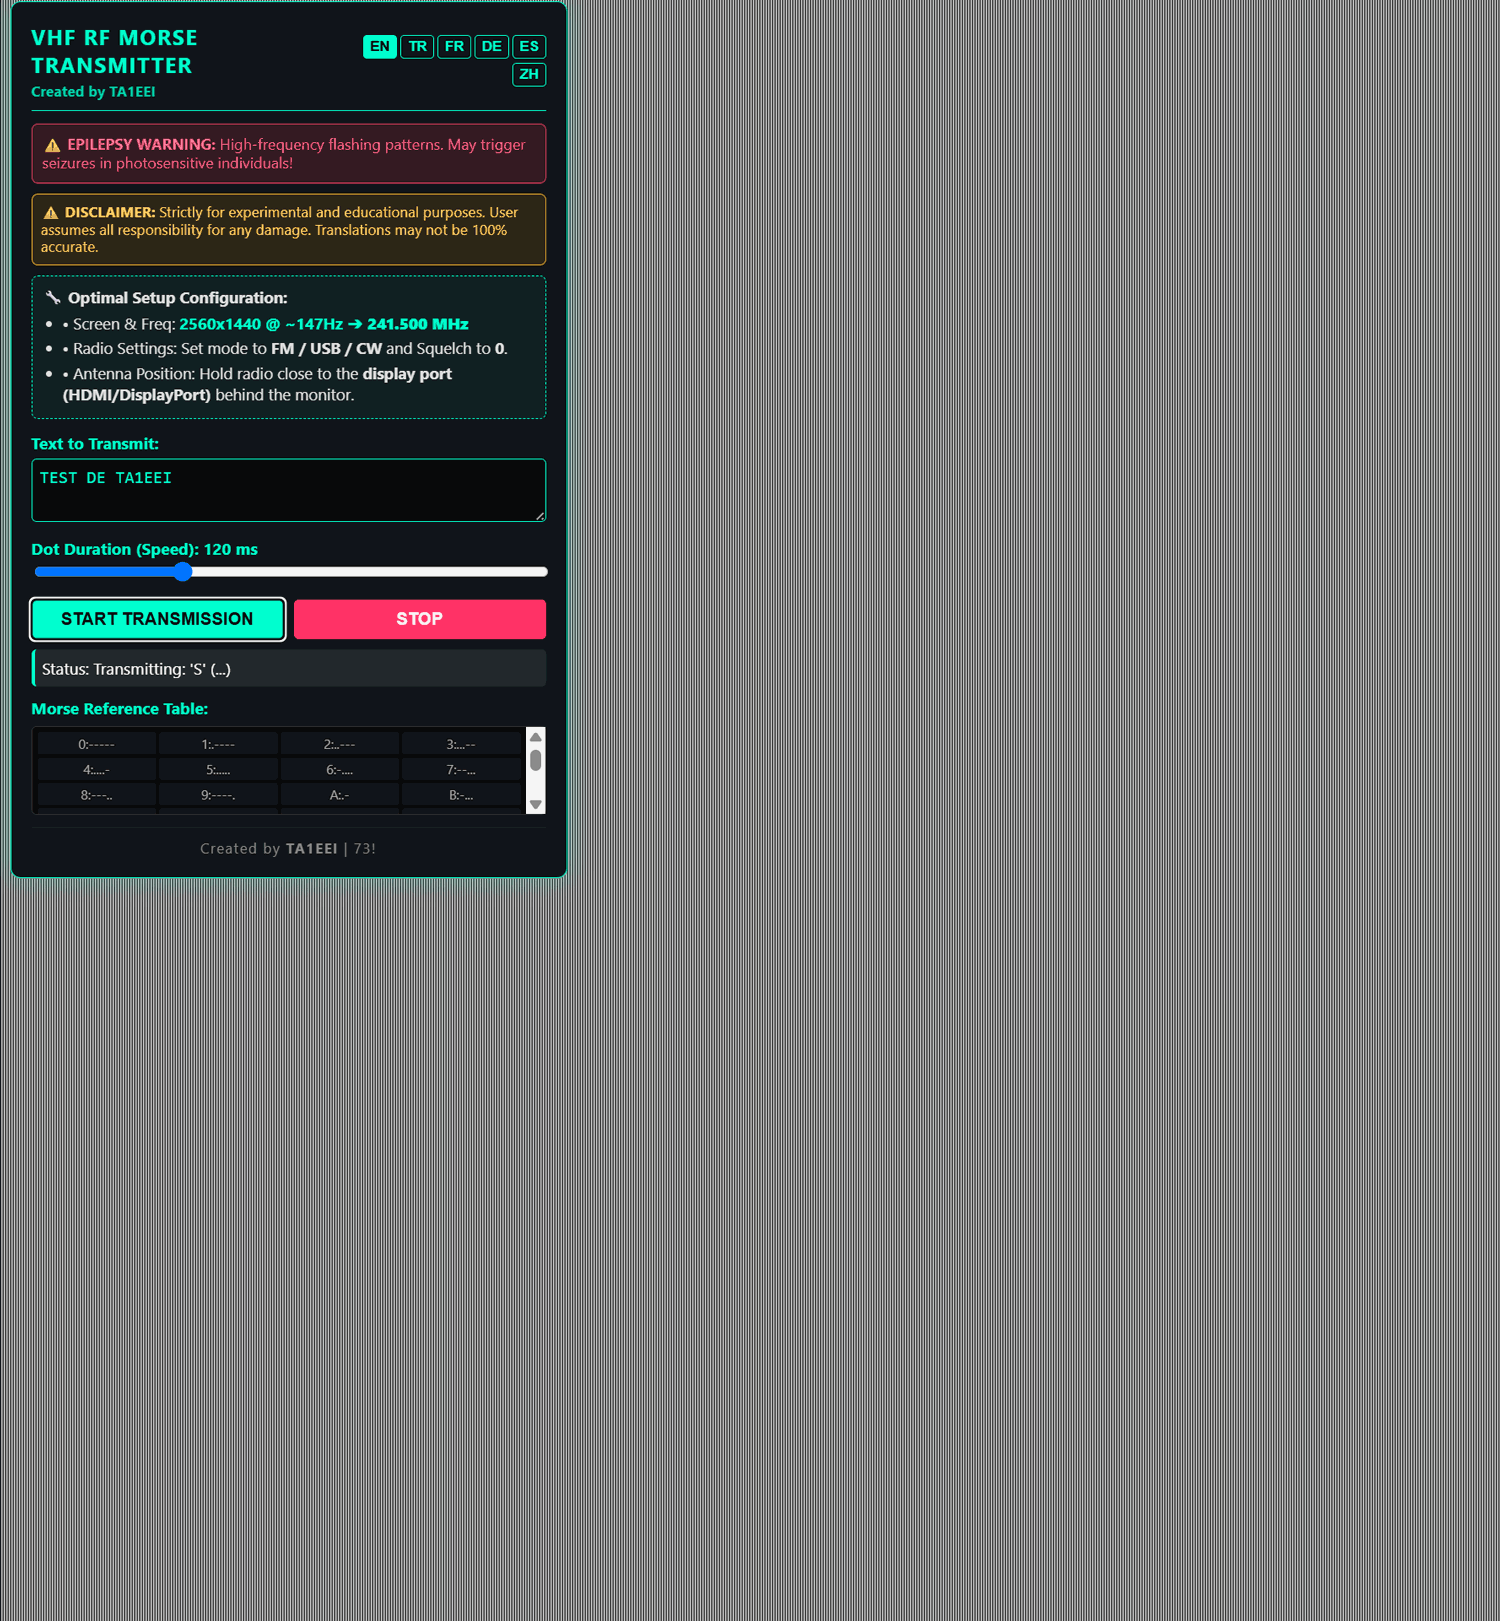
Thank you to Efe (TA1EEI) for writing in and sharing an HTML web tool he created that uses a PC monitor to transmit Morse code. The tool works by modulating the monitor's pixel clocks to intentionally generate EMI leakage in the form of a Morse code signal. It transmits at 148.5 MHz.

Efe's work appears to be a much simpler version of TrojPix, a University research project that we posted about back in July. TrojPix is a more advanced system that introduces imperceptible pixel modulations into the screen, making high-bandwidth wireless data transfer possible via monitor EMI leakage.

The GitHub project page for Efe's VHF Monitor RF Transmitter explains exactly how the project works, including the video pixel clock and how it can be modulated and transmitted wirelessly. Efe has also provided a link to a Reddit post where there is a video, and discussion. 

VHF Morse Code Transmitted via an HTML Page

TrojPix: Covertly Transmitting Data from Air-Gapped Systems via Video Cable Emissions

Researchers from the University of Shandong have recently demonstrated in a paper that they can transmit data from an air-gapped PC by using a Trojan to implement imperceptible pixel modulation in a monitor.

Every electronic device unintentionally emits RF, and PC monitors, TVs, and screens are no exception. In the past, we have shown that with simple TEMPEST tools, it is easy to recover the image on a screen over a distance using an RTL-SDR or Airspy SDR.

TrojPix relies on the unintentional emitted RF from a PC monitor's video cable. By subtly modulating the pixels on a screen, it is possible to enable data transfer via the unintentional emissions. This means that any PC infected with the TrojPix Trojan could transfer data wirelessly to a snooper, even if the PC is totally disconnected from any wired or wireless network. The only way to stop such an attack would be to completely shield the PC with a faraday cage.

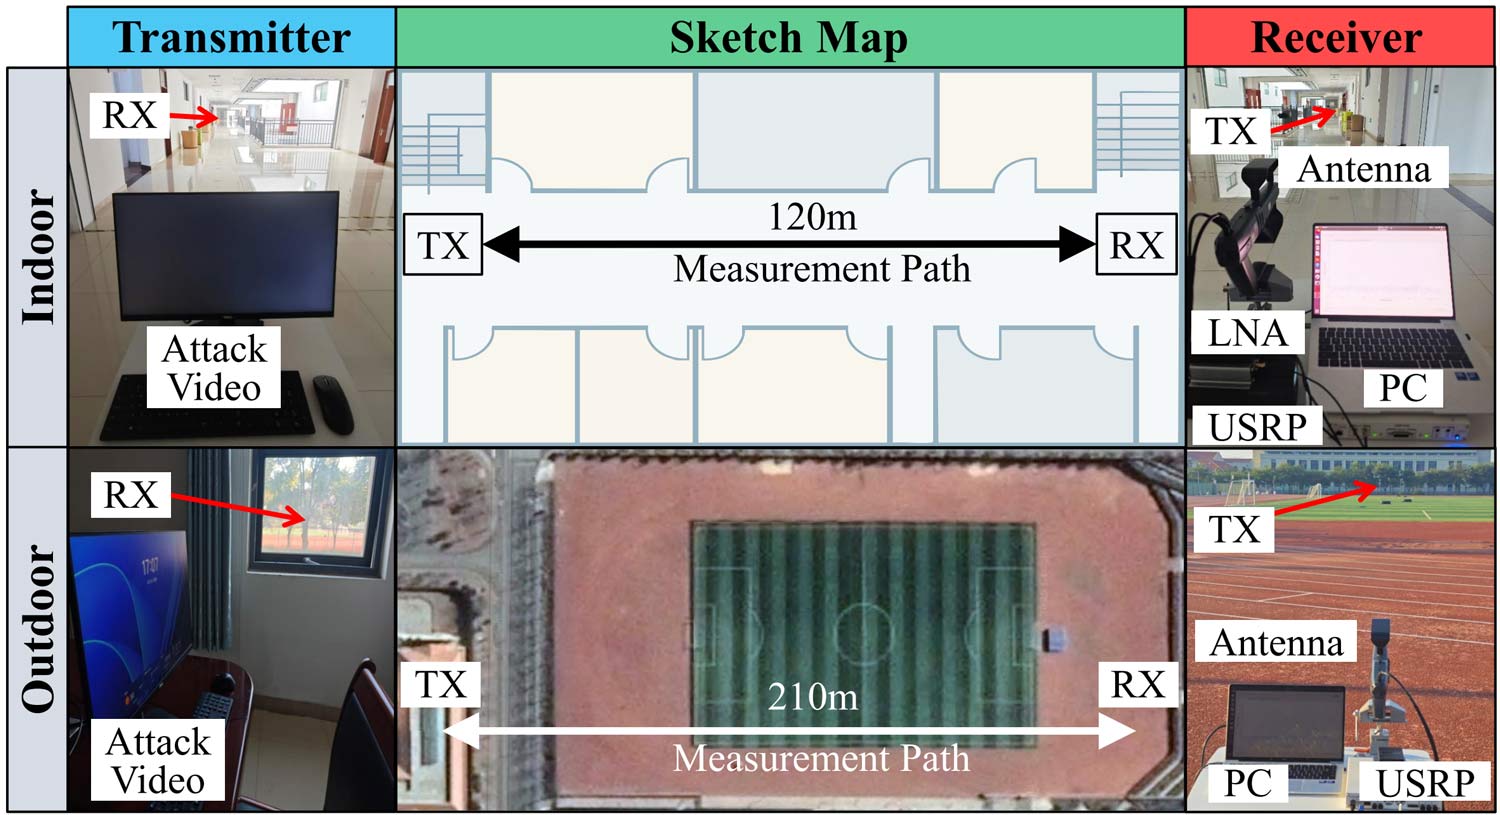
The team note that they were able to achieve a peak data throughput of 8.1 MBps over a max range of 208 meters. They tested nine commercially available monitors and fifteen digital video cables, each demonstrating significant usable RF leakage.

The receiver hardware used was a USRP X310 software-defined radio sampling at 10 MHz and the transmissions appear to have been at 148.5 MHz and 297 MHz.

TrojPix Experiment: Receiving Data over 210 neters,.

TEMPEST-LoRa: Emitting LoRa Packets from VGA or HDMI Cables

University researchers from China have recently shown in a research paper that it is possible to maliciously cause a VGA or HDMI cable to emit LoRa compatible packets by simply displaying a full-screen image or video. This has potential security implications as a malicious program could be used to leak sensitive information over the air, completely bypassing any internet or air-gap security systems.

In the past, we have demonstrated that TEMPEST techniques can be used to spy on monitors and security cameras by analyzing the unintentional signals they emit. This research takes the idea a step further by determining what particular images need to be displayed to create a LoRa packet with data. 

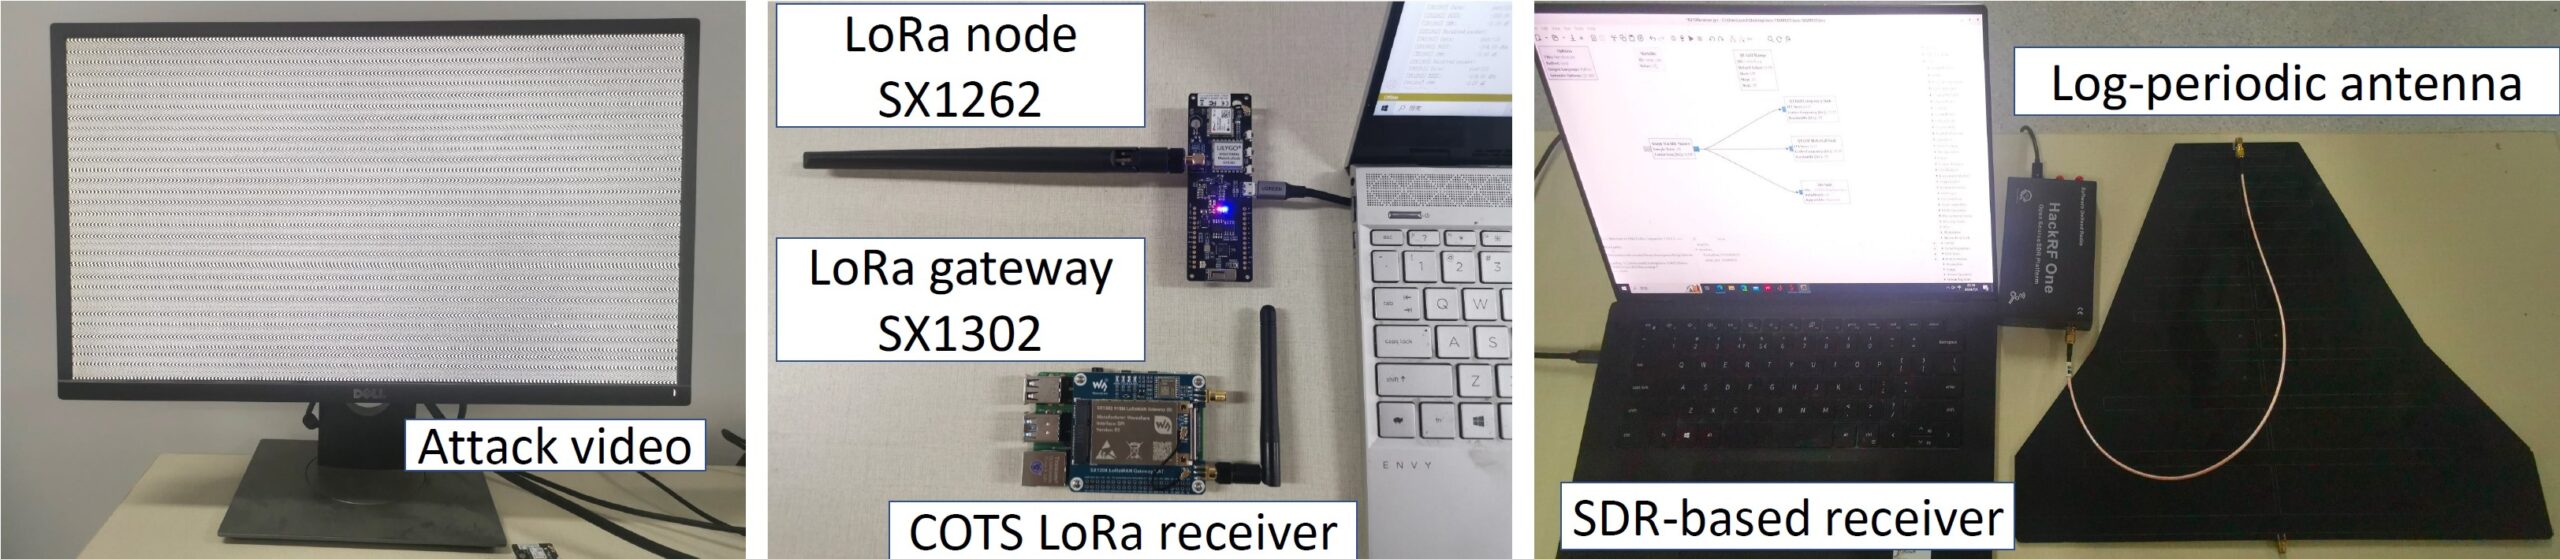
In the paper, the researchers mention using either off-the-shelf LoRa devices or low-cost SDRs such as the HackRF to receive the packets. The advantage of the SDR method is that it allows for customization of the frequency and the use of LoRa-like packets, which can achieve even longer ranges and higher data rates. The team show that they were able to achieve a receive range of up to 132 meters and up to 180 kbps of data rate.

TEMPEST-LoRa Test Setup
(Demo video) TEMPEST-LoRa: Cross-Technology Covert Communication

HackRF and Portapack Featured in Recent Linus Tech Tips Video

Over on YouTube the Linus Tech Tips channel has recently released a video about the HackRF titled "It’s TOO Easy to Accidentally Do Illegal Stuff with This". Linus Tech Tips is an extremely popular computer technology YouTube channel. The HackRF is a popular transmit capable software defined radio that was released about 10 years ago. The portapack is an add-on for the HackRF that allows the HackRF to be used as a handheld device, and when combined with the Mayhem firmware, it enables easy access to some controversial tools that could get a user into a lot of legal trouble very fast.

In the video Linus, whose team is based in Canada, mentions that they decided to purchase the HackRF and similar devices because of the Canadian government's plan to ban various RF tools, including the Flipper Zero and HackRF.

Linus then discusses and demonstrates "van eck phreaking" with TempestSDR, showing how he can use the HackRF to recover the video from a PC monitor wirelessly. He then goes on to demonstrate how the Portapack can be used to jam a wireless GoPro camera transmitting over WiFi. 

Finally, Linus discusses the legality and morality of such devices being available on the market.

It’s TOO Easy to Accidentally Do Illegal Stuff with This

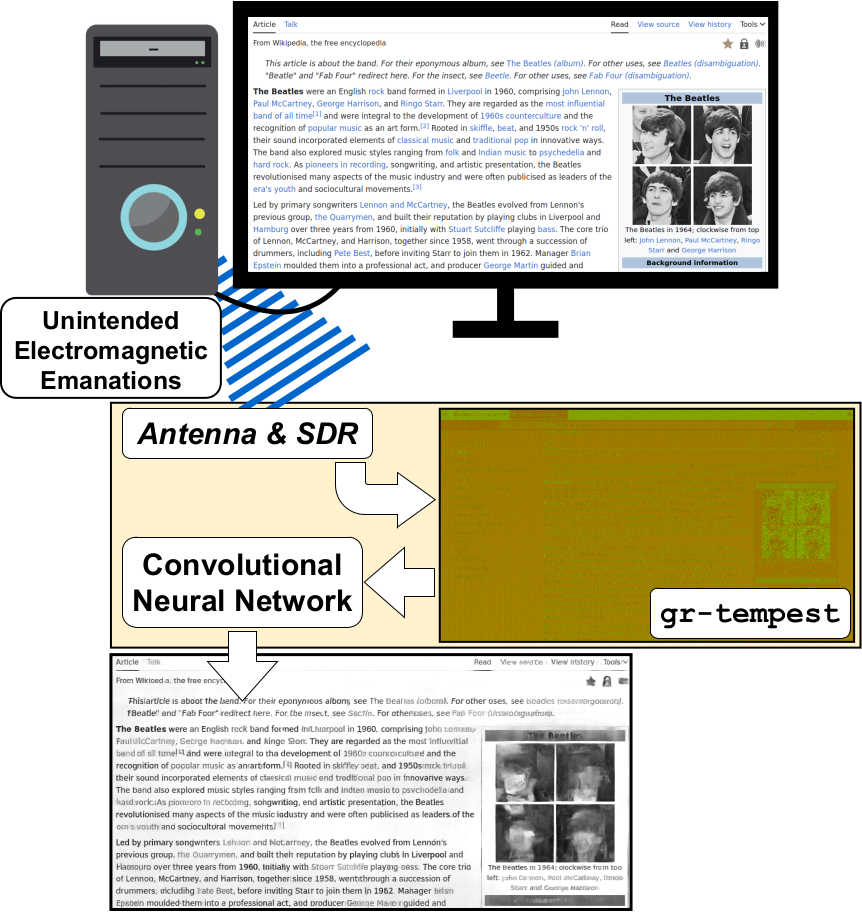
Deep-Tempest: Eavesdropping on HDMI via SDR and Deep Learning

Over the years we've posted several times about the TEMPEST applications of software-defined radio. TEMPEST aka (Van Eck Phreaking) is when you listen to the unintentional RF emissions of electronics and are able to recover information from that. In the past, we posted about TempestSDR, an RTL-SDR compatible program that allows you to view images from a computer monitor or TV simply by picking up the unintentional RF emissions from it.

Usually, the images received are fuzzy and it can be difficult to recover any information from them. However recently there has been work on combining Tempest techniques with deep learning AI for improving image quality.

Deep-tempest has recently been released on GitHub and from their demonstrations, the ability to recover the true image with deep learning is very impressive. From a fuzzy grey screen, they show how they were able to recover clear text which looks almost exactly like the original monitor image.

Deep-tempest is based on gr-tempest, and requires GNU Radio, Python 3.10 and a Conda environment. Instructions for installing it are on the GitHub.

The whitepaper on the University research done to implement Deep-Tempest can be found freely on arxiv at https://arxiv.org/pdf/2407.09717.

How Deep-Tempest Works
Deep-Tempest Results

Snooping Network Traffic from LAN Cables with an RTL-SDR or HackRF

Mordechai Guri is a cyber-security security researcher at Israel's Ben Gurion University of the Negev. Recently Guri has described a method for sniffing network data from LAN Ethernet cables over an air gap through the use of RTL-SDR or HackRF software defined radios. Guri's paper is available directly here.

The idea behind the attack is that ethernet cables can act as an antenna, leaking signals at frequencies which can easily be sniffed by a SDR. The specific technique in the paper does not decode normal network traffic, instead it requires that malicious code which modulates a custom signal over the ethernet cable be installed on the PC first. The technique used appears to be similar to what the Etherify software by SQ5BPF uses, which modulates data in morse code by turning the network card on and off.

Receiving a signal modulated by the LanTenna malware