Live TEA1 Decryption Support Added to an osmo-tetra Fork
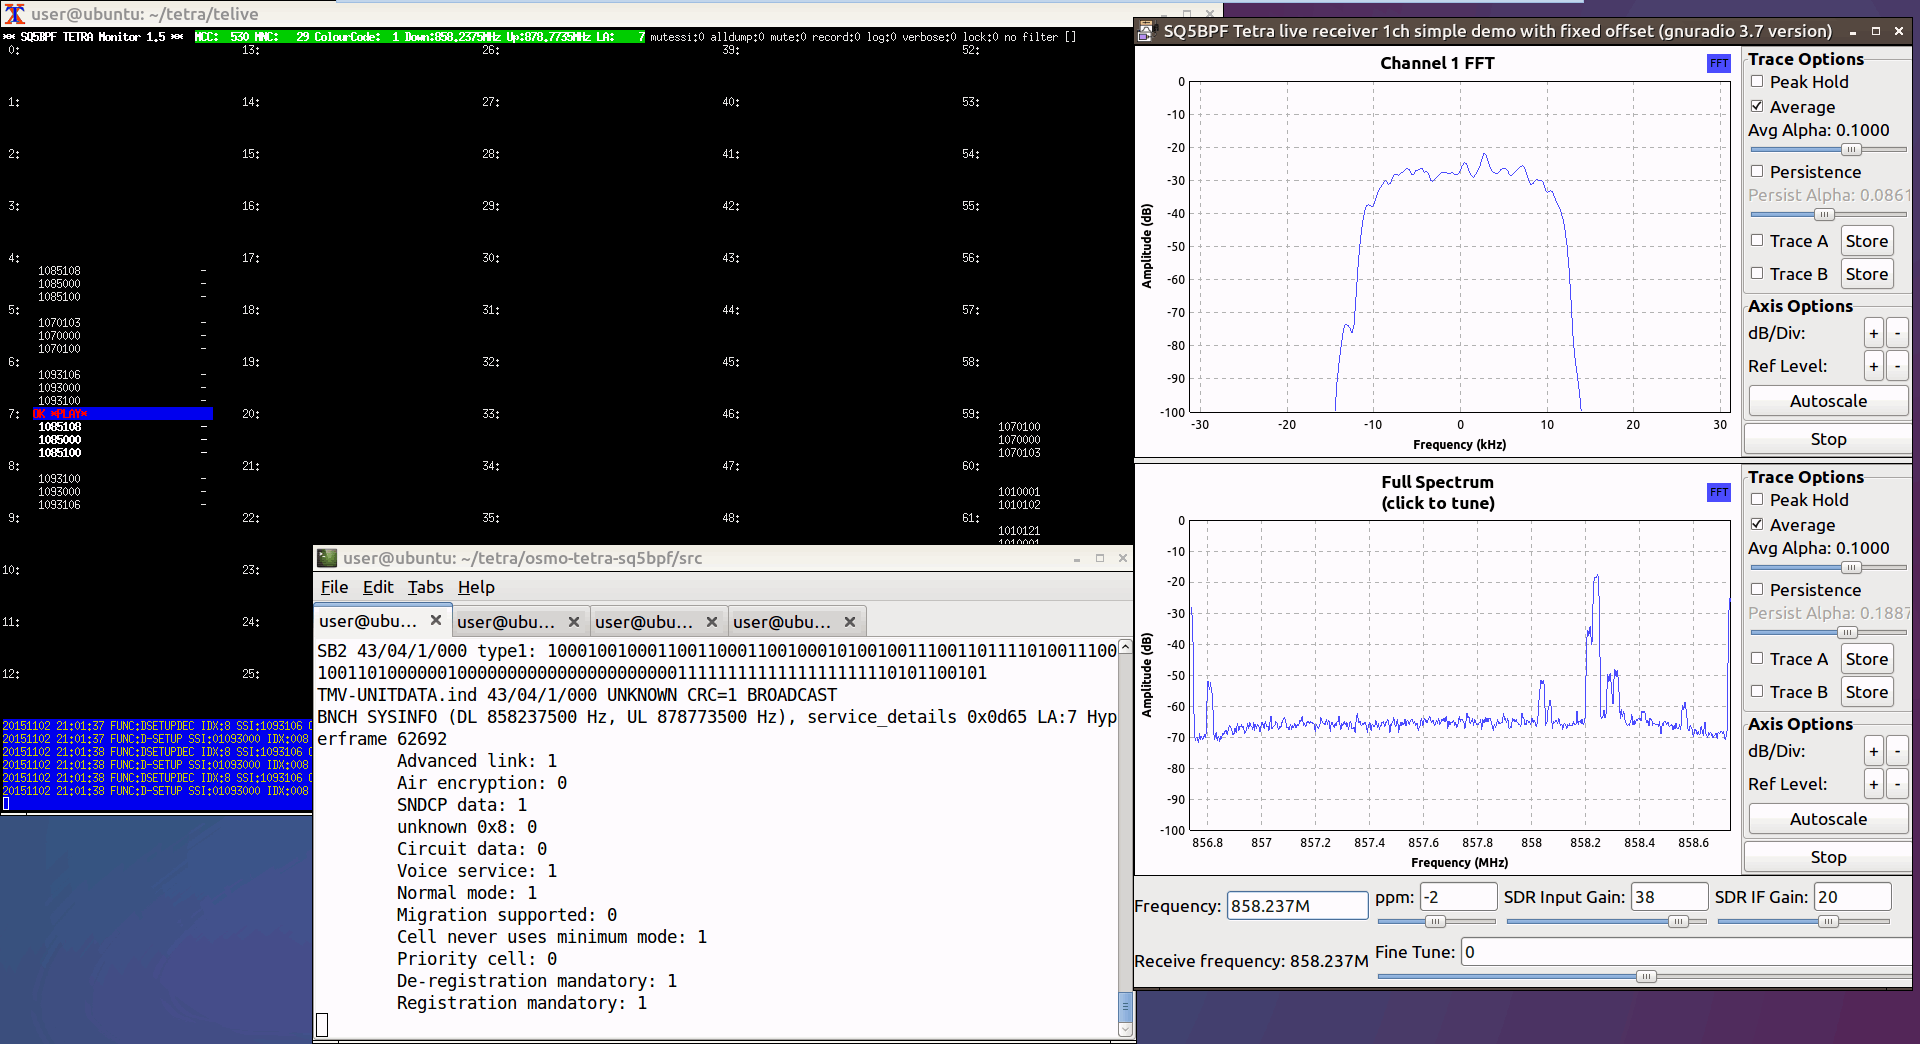
Over on GitHub, su4am has published a fork of the well-known osmo-tetra-sq5bpf TETRA decoder that integrates TEA1 cipher support based on CVE-2022-24402. Back in 2023, we first posted about the TETRA TEA1 vulnerability discovery. Midnight Blue, a security research team, discovered this vulnerability as part of their TETRA:BURST research. The discovery found that a key-scheduling flaw reduces the effective keyspace from an impossible-to-brute-force 2^80 down to 2^32, which is small enough to brute force in a few minutes on a commodity GPU. This fork combines the osmo-tetra-sq5bpf TETRA decoder with Midnight Blue’s TETRA_crypto library so that recovered 32-bit keys are applied on the fly to encrypted voice bursts directly inside the decoder.
Importantly, we note that the fork does not crack keys by itself. The tetra-rx decoder outputs “key recovery candidate” tuples from the air, which you then feed into a separate GPU tool (SQ5BPF’s teatime) to actually brute force the reduced keyspace. Recovered keys are added to a keyfile and loaded live, so decryption begins on the next burst without restarting the pipeline. The fork also adds a dual-socket TRA output, letting you monitor decrypted and unencrypted traffic simultaneously with two telive-2 instances.
We want to warn that intercepting or decrypting communications you are not authorized to receive is illegal in most countries.