Tagged: security

InjectEave: Eavesdropping on Headphones by Injecting a Carrier and Listening to the Modulated Retransmission

Researchers from the Hong Kong University of Science and Technology (Guangzhou) and the Hong Kong Polytechnic University recently published a paper titled "Injected and Leaked: Actively Inducing Side-Channel Leakage Using Electromagnetic Injection and Hardware Nonlinearity".

The paper describes how an attacker can use a directional antenna to transmit a carrier signal toward an electronic device, where nonlinearities in its components modulate the signal, which connected cables then re-radiate as unintentional antennas. The attacker can then receive the modulated carrier at the same frequency as it is transmitted and demodulate the modulated sidebands.
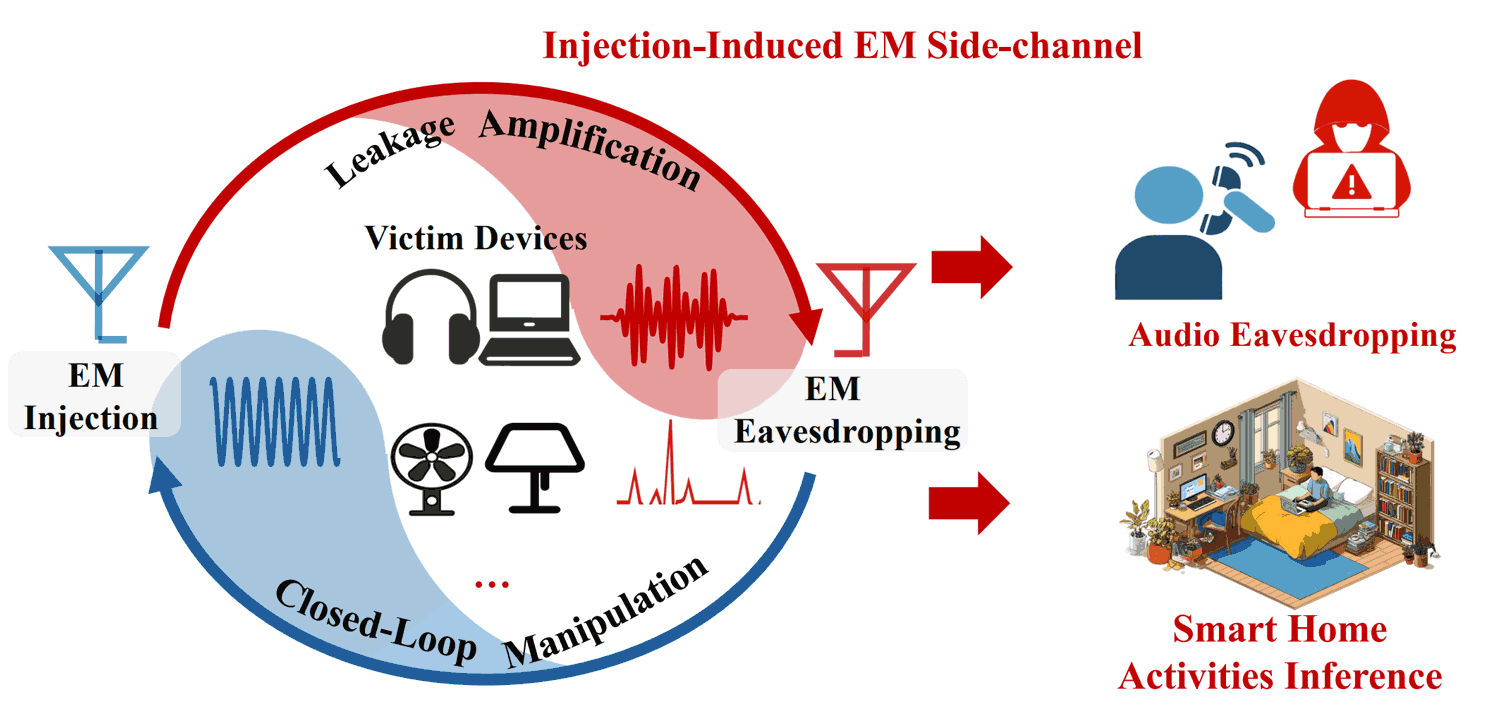
The Injecteave Process

In their experiments, they used a USRP B210 software-defined radio to transmit the CW injection signal at anywhere from 0 to 8 MHz (the exact frequency for a device is not specified in the paper for ethical considerations), and a spectrum analyzer to receive the injection-induced EM leakage. The spectrum analyzer demodulates the received mixed signal, then routes the baseband to a PC for further processing. They show how various wired and wireless headphones exhibited injection-induced leakage via the amplifier, and how landline desk phones, smart fans, and lamps were also susceptible.

They also show a real-world application where they eavesdropped on audio from headphones and desk phones through walls in a hotel, meeting room, and office.

Update: Thanks to a commenter for pointing out the InjectEave demo page at https://injecteave.github.io.
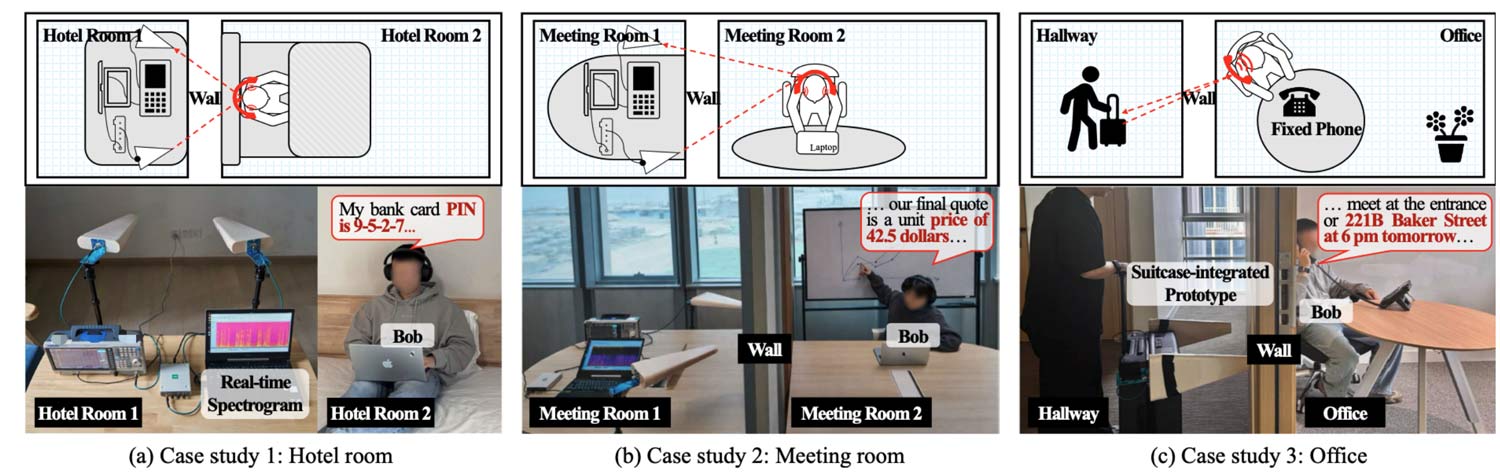
InjectEave: Real World Examples

More Information about the FrameRF Technical Surveillance Counter-Measures Platform – Technical Guest Post

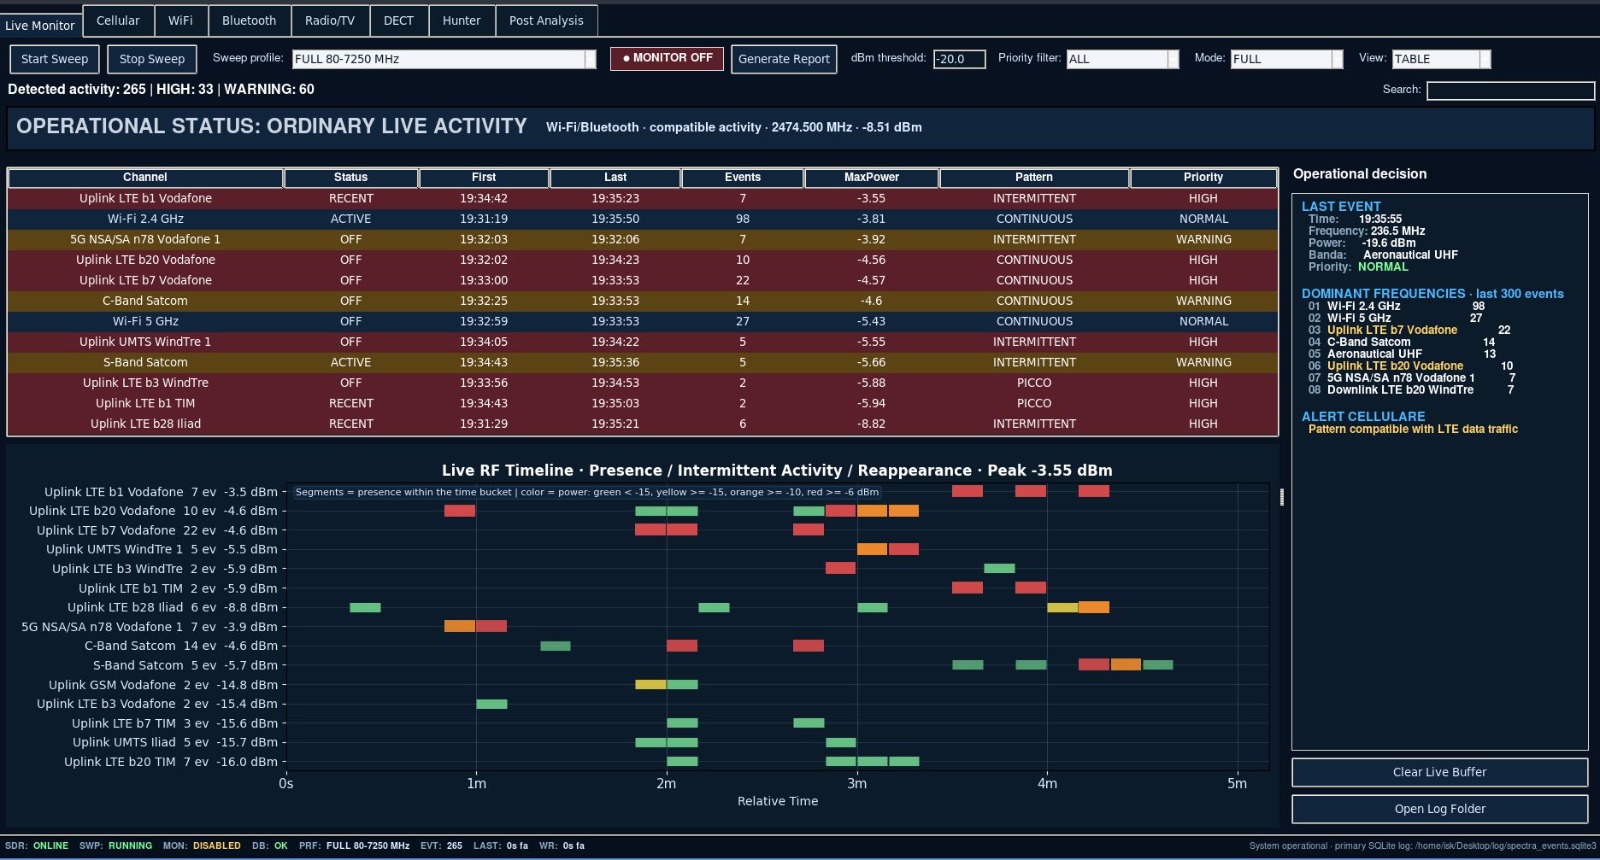
Earlier this month, we posted about Stefano Cangiano, an Italian TSCM (Technical Surveillance Counter-Measures) specialist, and his recently released FrameRF product. Stefano describes FrameRF as "a professional SDR-based TSCM analysis platform designed to help operators rapidly identify, classify, and prioritize RF signals in complex environments." Its main use case is for identifying RF bugs, corporate security audits, and finding anomalous signals.

Recently, Stefano wrote in again and wanted to share some further technical details about his product. Stefano notes that the core idea of FrameRF is to solve the TSCM question: "What happened in the RF environment over the last few hours, and how did it behave?" The system logs RF activity as timestamped events across cellular, Wi-Fi, BLE, DECT, and other signals, correlates them with physical events, and highlights anomalies and intermittent transmitters like event-triggered GPS trackers as leads for further investigation.

Stefano's full write-up is available as a PDF, which you can download here.

The FrameRF Product
The FrameRF Product

ESP32 Bit Pirate Updates: New LoRa and Meshtastic Analysis Features

Back in September 2025, we posted about the "ESP32 Bus Pirate" firmware, which transforms an ESP32-S3 into a multi-protocol debugging and hacking tool. We later covered an update in March 2026 that added waterfall displays, cellular modem support, and an external radio expander.

Although the ESP32 does not have true SDR capabilities, it can leverage its numerous built-in radio hardware components to achieve a range of interesting SDR-like features. Recently, "Geo," the creator of the ESP32 Bus Pirate, wrote in to share some recent firmware updates with us.

Geo notes that the project is now called "ESP32 Bit Pirate" and now includes LoRa/SX1262 support and Meshtastic analysis features.

ESP32 Bit Pirate can now transmit and receive LoRa packets, monitor RSSI, scan frequency activity, display a simple waterfall view and perform Channel Activity Detection. Radio parameters including frequency, bandwidth, spreading factor, coding rate, transmit power, preamble and sync word can be configured directly from the interface.

Packets can also be recorded to the ESP32 filesystem and replayed later together with their original radio configuration.

A dedicated Meshtastic analysis shell has also been added, allowing users to send, receive and inspect Meshtastic packets. The goal is not to replace a Meshtastic node, but to provide a debugging and experimentation interface for understanding and interacting with LoRa/Meshtastic traffic.

The latest update has also added new LoRa hardware support for the Heltec Vision Master T190 and Heltec WiFi LoRa 32 V4, a browser-based debugging ecosystem, a Python scripting lab, and a BPIO2 USB adapter mode.

The project is entirely open source, and the code can be found on their GitHub page.

ESP32 Bit Pirate LoRa Support Added

FrameRF: An SDR-Based Technical Surveillance Counter-Measure Analysis Platform

Thank you to Stefano Cangiano, an Italian TSCM (Technical Surveillance Counter-Measures) specialist, for writing in and sharing with us about the release of his FrameRF product. Stefano writes:

After more than ten years of operational field experience, I developed FrameRF, a professional SDR-based TSCM analysis platform designed to help operators rapidly identify, classify and prioritize RF signals in complex environments.

Rather than replacing existing SDR software, FrameRF focuses on operational analysis by correlating multiple wireless technologies (Wi-Fi, Bluetooth, BLE, GSM, LTE and others) into a single workflow that supports real-world investigations.

FrameRF has been developed from real operational TSCM field experience, with the goal of reducing RF analysis time and helping operators make faster and more informed decisions during technical inspections.

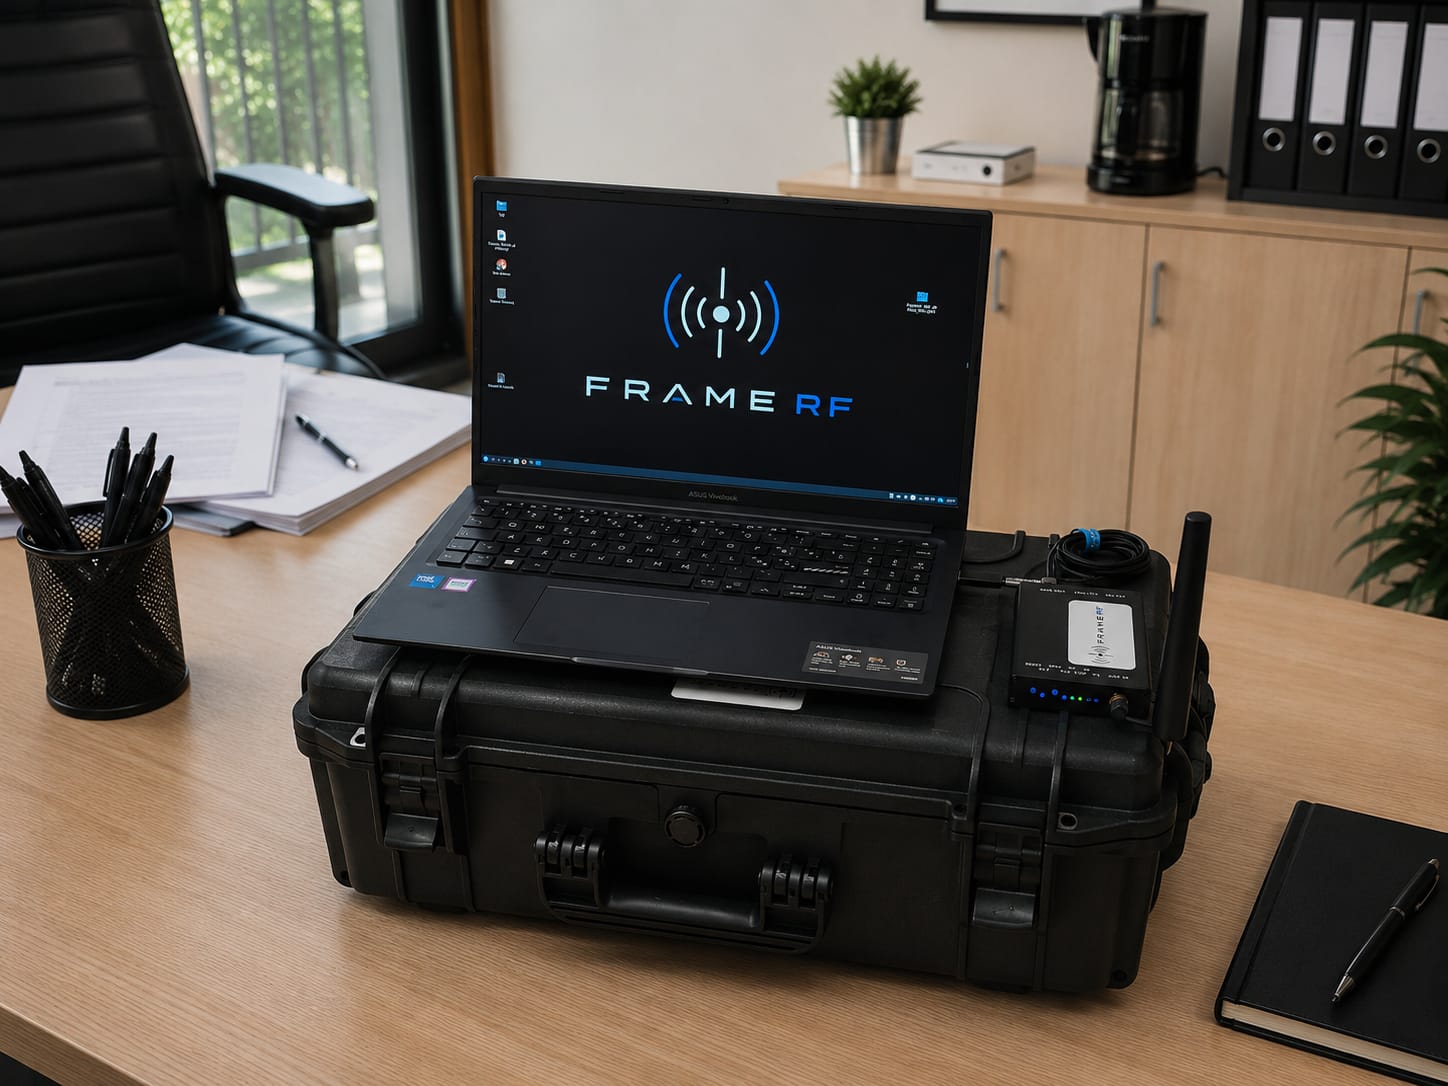
To summarize, FrameRF appears to be a portable deployable kit, consisting of a laptop, SDR hardware, antennas, and custom software in a rugged briefcase. The product is intended to be used by TSCM specialists for applications like sweeping for RF bugs, corporate security audits, and finding anomalous signals.

It can do things like detect LTE voice activity, automatically classify signals, alert the user based on patterns, detect a DECT phone call, recognize Apple AirTags, estimate if different random Bluetooth MAC addresses belong to the same physical device, analyze the WiFi environment, reconstruct device relationships, and detect hidden WiFi networks and potential spoofing.

If you are interested, Stefano has provided a PDF brochure explaining the product further.

FrameRF Live Monitor
FrameRF – Professional RF Behavioral Analysis Platform | TSCM Video Demonstration

TrojPix: Covertly Transmitting Data from Air-Gapped Systems via Video Cable Emissions

Researchers from the University of Shandong have recently demonstrated in a paper that they can transmit data from an air-gapped PC by using a Trojan to implement imperceptible pixel modulation in a monitor.

Every electronic device unintentionally emits RF, and PC monitors, TVs, and screens are no exception. In the past, we have shown that with simple TEMPEST tools, it is easy to recover the image on a screen over a distance using an RTL-SDR or Airspy SDR.

TrojPix relies on the unintentional emitted RF from a PC monitor's video cable. By subtly modulating the pixels on a screen, it is possible to enable data transfer via the unintentional emissions. This means that any PC infected with the TrojPix Trojan could transfer data wirelessly to a snooper, even if the PC is totally disconnected from any wired or wireless network. The only way to stop such an attack would be to completely shield the PC with a faraday cage.

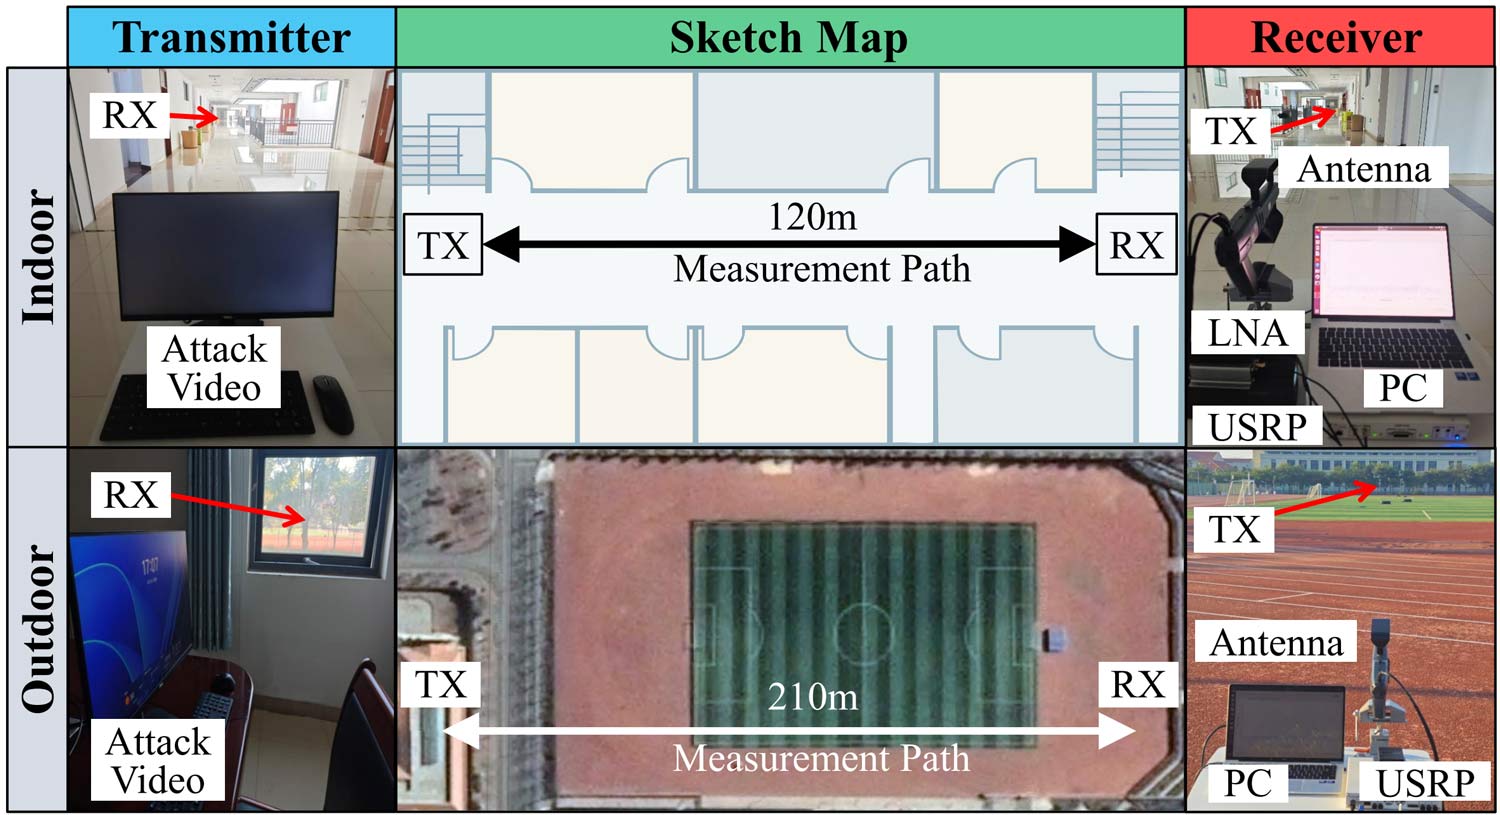
The team note that they were able to achieve a peak data throughput of 8.1 MBps over a max range of 208 meters. They tested nine commercially available monitors and fifteen digital video cables, each demonstrating significant usable RF leakage.

The receiver hardware used was a USRP X310 software-defined radio sampling at 10 MHz and the transmissions appear to have been at 148.5 MHz and 297 MHz.

TrojPix Experiment: Receiving Data over 210 neters,.

Student Arrested in Taiwan for using SDR and Handheld Radios to Halt Four High Speed Trains with TETRA Hack

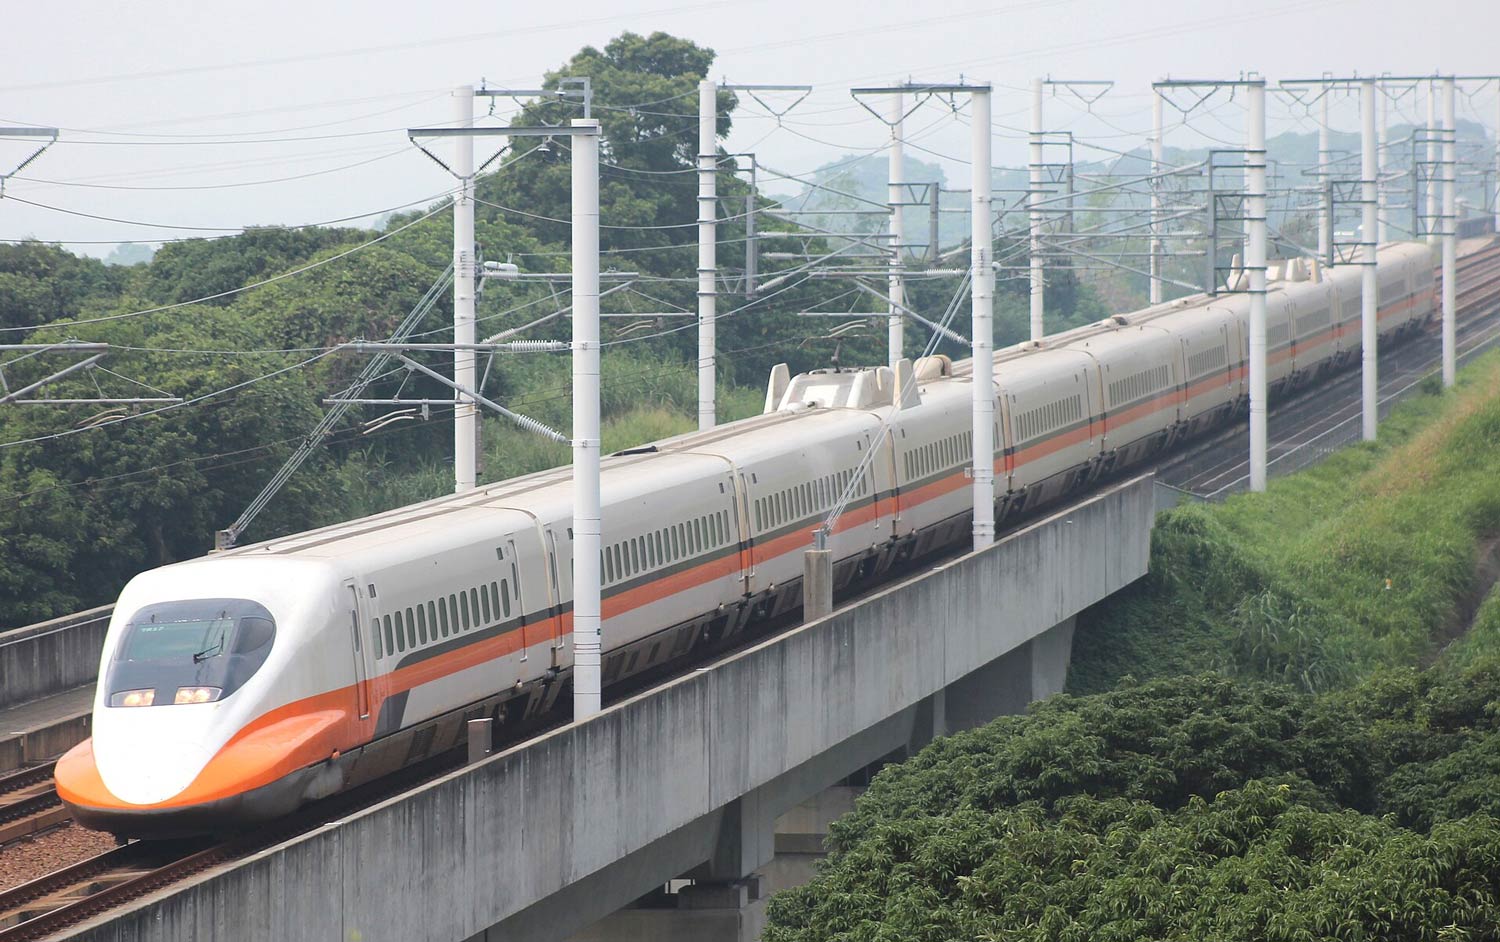
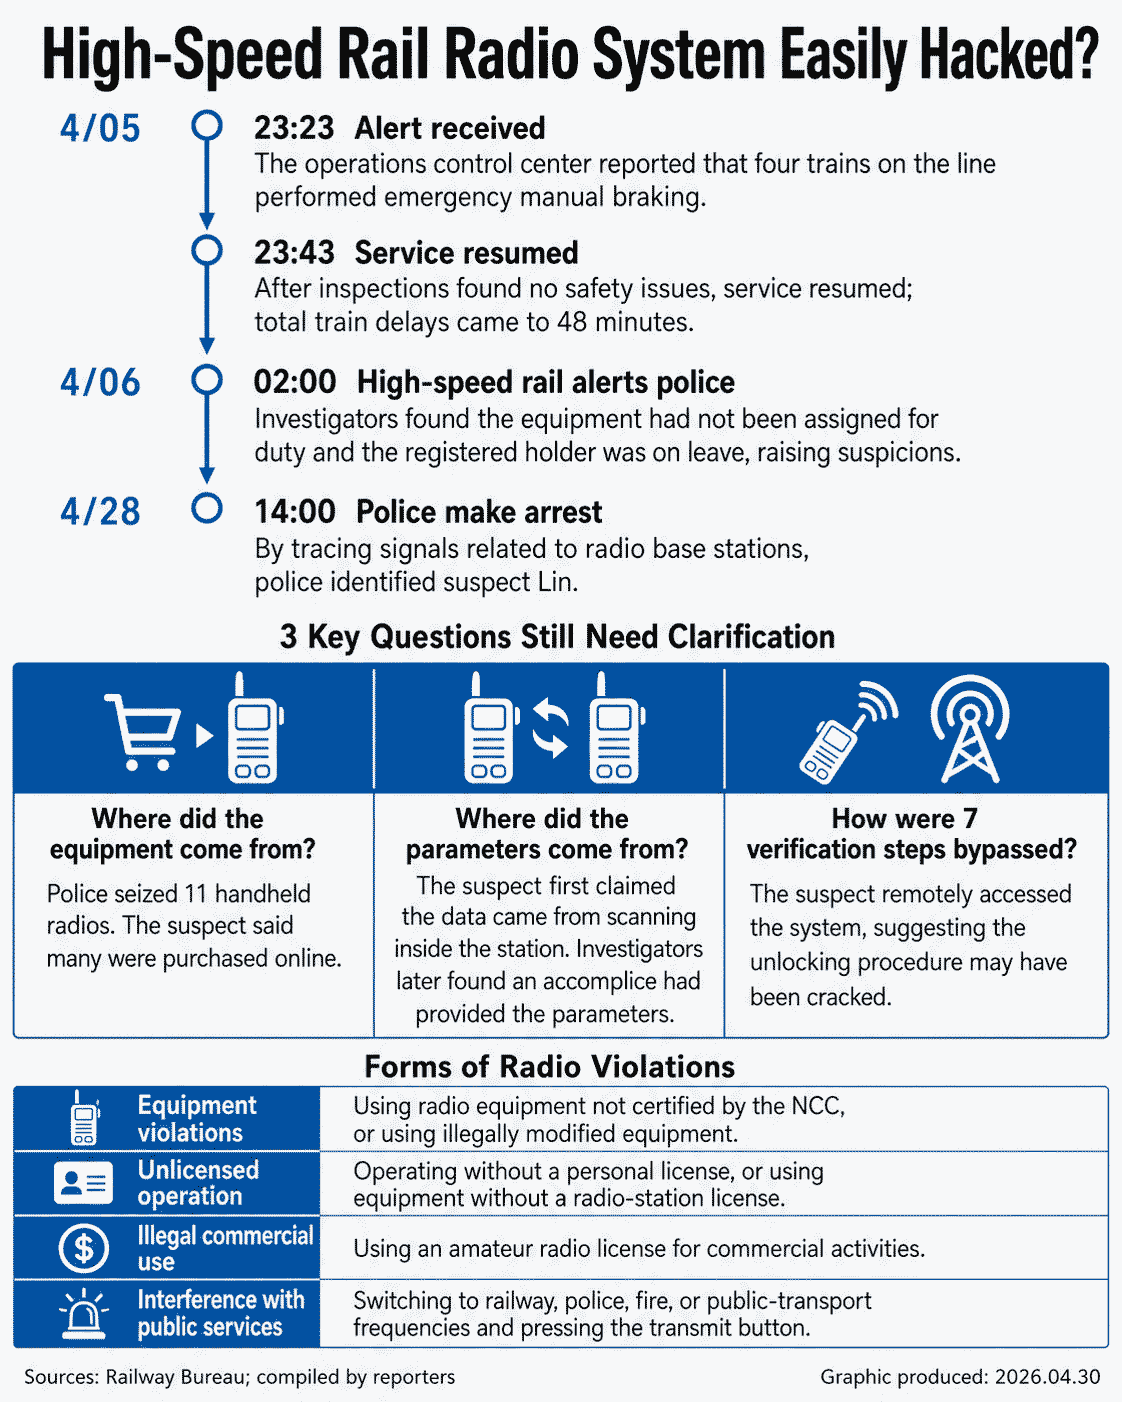
The Taipei Times has reported that a 23-year-old university student in Taiwan has been arrested after using a software-defined radio and hand held radio to hack into Taiwan High Speed Rail Corporation's (THSRC) internal radio communications and halt four trains mid-service.

Chinese-language coverage from UDN and Newtalk fills in some details omitted in the English Taipei Times article. The system the student compromised is TETRA, and at 23:23 on April 5, 2026, the student transmitted a "General Alarm" (GA) signal, the highest-priority TETRA alert, which automatically instructs trains in the area to switch to manual emergency braking. Four trains were stopped for 48 minutes. THSRC's radio system has reportedly been in service for 19 years with seven verification layers, but parameters were apparently never meaningfully rotated over that period.

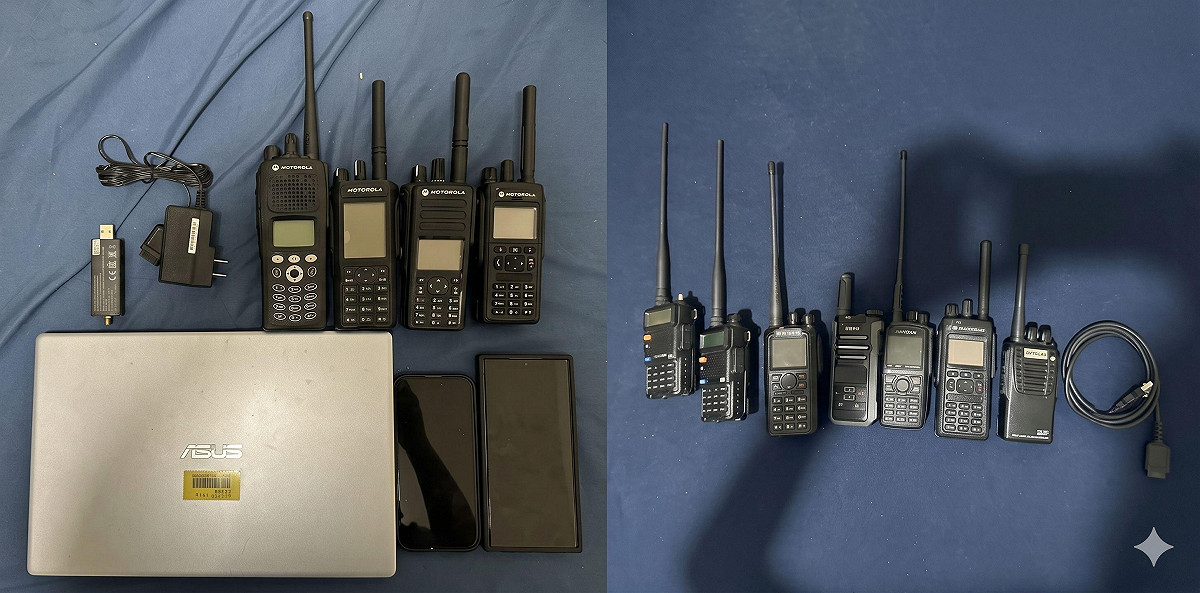
Police describe the suspect as buying an SDR online, connecting it between an antenna and a laptop, capturing THSRC traffic, and decoding the relevant parameters in software, then programming those parameters into one of his eleven handheld radios. A 21-year-old friend also allegedly supplied some critical THSRC parameters. The actual details of the 'hack' aren't entirely clear from the news articles. We suspect that the THSRC TETRA system is simply unencrypted, and that the student was able to spoof a legitimate signal. It's also possible that the THSRC TETRA system used TEA1 encryption, which is known to be broken

Police located the student through a combination of network-side TETRA logs and CCTV. When the THSRC control center called back to verify the alarm, the person on the other end gave contradictory answers and then powered the radio off, prompting THSRC to audit their handheld fleet, confirm every issued radio was accounted for in its storage locker, and report to police that the parameters had been cloned.

Base station logs from the THSRC TETRA infrastructure (which record which sites received the uplink, with multi-site signal strength narrowing the origin) were used to localize the transmission source, and CCTV from around the coverage area was then used to identify the student and trace him to his rental unit. Search warrants on 28 April seized 11 handheld radios, a laptop, and the SDR. 

He is currently out on NT$100,000 (3,200 USD) bail and faces up to ten years under Taiwan's Railway Act and Criminal Code, with an unconvincing "had it in my pocket and accidentally pressed the button" defense.

Stories like this are a reminder that experimenting with operational safety-of-life radio systems carries serious legal consequences. Back in 2016, we covered the case of Dejan Ornig, a Slovenian university student who used an RTL-SDR and the open source Osmocom TETRA decoder to discover that his country's police TETRA terminals were running unauthenticated, despite official documents stating otherwise. After seven years of court hearings, he ended up with a seven-month suspended sentence. More recently, we posted on the End of Train (EoT) vulnerability, where a security researcher demonstrated that an SDR can replicate the unauthenticated braking command on US freight trains.

The Equipment Seized by Police
A Taiwanese High Speed Train (Source: https://en.wikipedia.org/wiki/File:THSR_700T_TR17_20130907.jpg)
Translated news graphic from https://udn.com/news/story/7315/9475450

Detecting Hidden GPS Trackers via Electromagnetic Unintentional Emissions with a HackRF

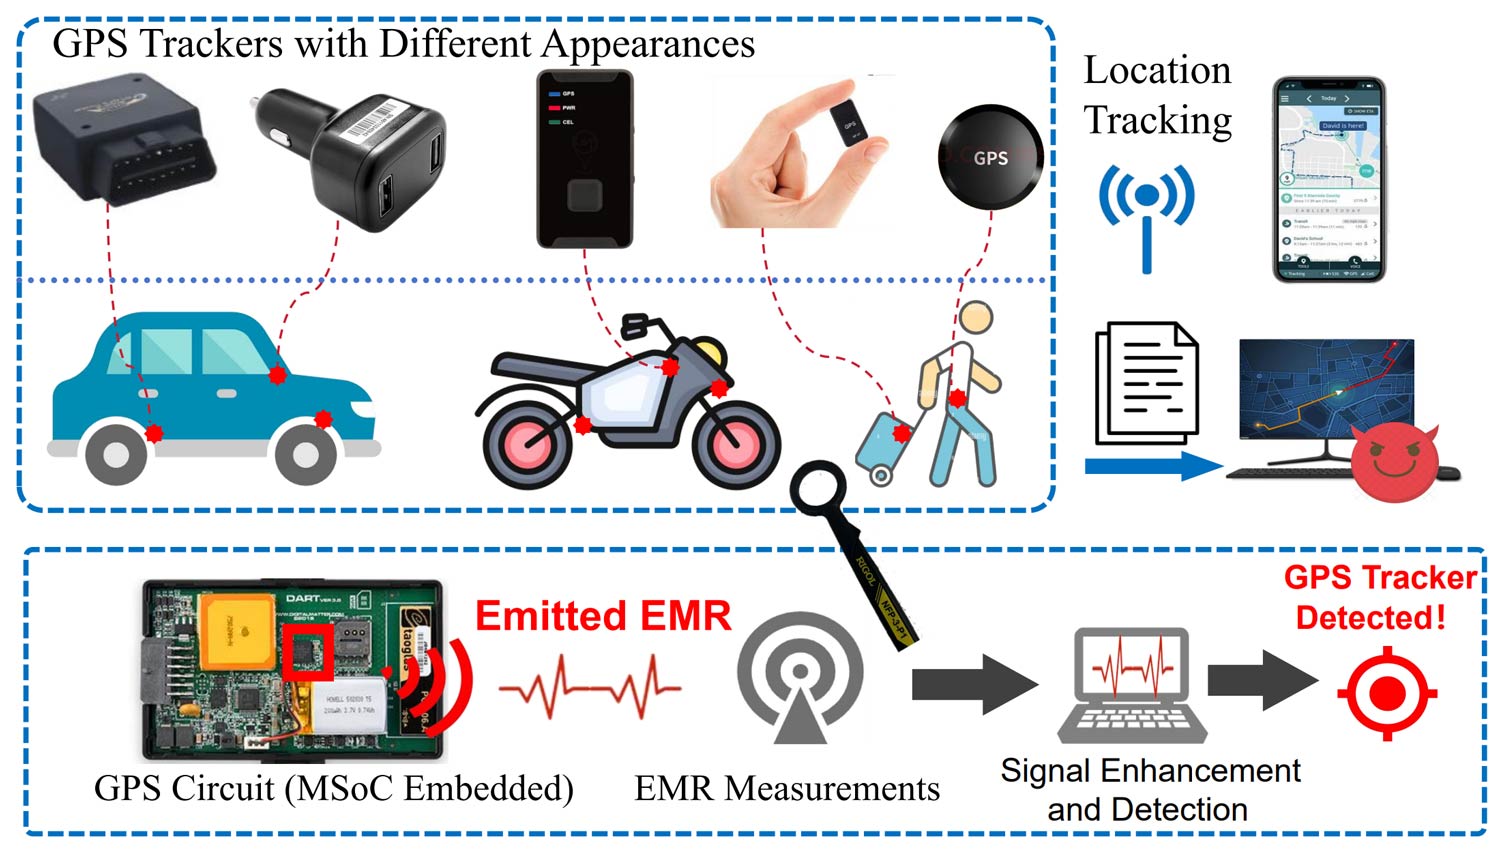
Researchers from Hunan University, Boise State, and UT Arlington have published a paper called "GPSBuster" (PDF link), demonstrating how a HackRF One can sniff out covert GPS trackers by their unintended electromagnetic radiation. Hidden trackers are hard to find since they only receive satellite signals and may store coordinates locally rather than transmit. Instead of looking for transmissions, GPSBuster targets side-channel leakage from the tracker's mixed-signal SoC, specifically the coupling between the quartz oscillator, local oscillator, and mixer used to downconvert the 1575.42 MHz L1 signal.

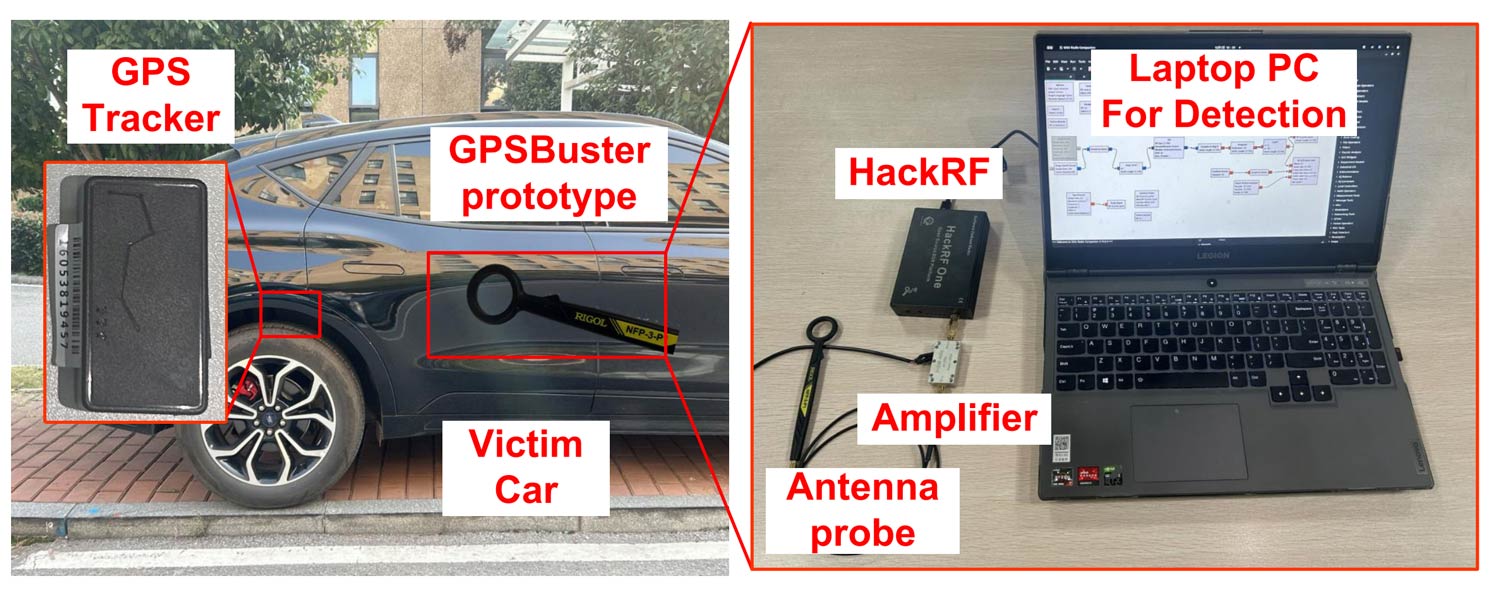
The team found that an active tracker leaks two characteristic spectra: a low band around 26 to 104 MHz and a high band around 1545 to 1625 MHz, each with a strong peak and evenly spaced harmonics. The low band reflects coupling between the quartz oscillator (typically 26 MHz) and the IF, while the high band contains LO plus IF spacing that always sums to 1575.42 MHz, giving a database-free detection rule. The setup consists of a HackRF, an NFP-3 near-field probe, and a 35 dB LNA. The use of the near-field probe means that sweeping the probe over an area to find the tracker is necessary, and the maximum detection range was 0.61 m.

Tested against the top 10 trackers available on a popular online marketplace, GPSBuster hit a 98.4% detection rate, working through plastic, cotton, canvas, and leather, and alongside phones, laptops, and speakers. It also extended to L1+L5 modules like the Quectel LC29H series, and even metal-shielded chips still leaked enough via PCB traces to be picked up.

Covert GPS Tracker Detection with a HackRF and Near Field Probe
GPSBuster Field Prototype

DeDECTive: A DECT 6.0 Cordless Phone Scanner and Voice Decoder for the HackRF

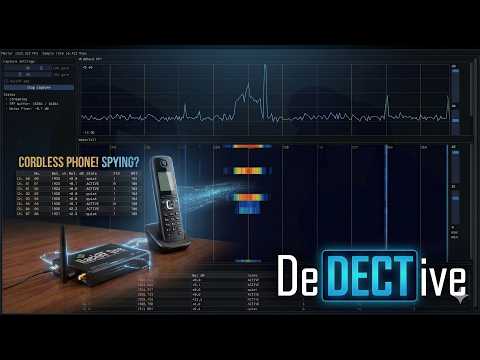
Over on GitHub and YouTube, we've seen the release of Sarah Rose's new program called DeDECTive, a DECT 6.0 scanner and voice decoder for the HackRF running on Linux systems. DECT (Digital Enhanced Cordless Telecommunications) is a digital wireless protocol typically used by modern cordless phones.

Back in 2019, Sarah (previously known as Corrosive) demonstrated how to use gr-dect2 to decode DECT in a previous video. In her latest work, she's ported gr-dect2 to C++ and written a nice GUI for the decoder. This makes running and setting up the decoder a significantly better experience. The GUI has a wideband scanner and the ability to tune for a single DECT channel for full voice decoding. There is also a CLI version that will automatically tune to the first active voice channel.

We note that many DECT cordless phones use encryption, so this software may not work with those devices. In any case, please be aware that intercepting phone calls may be illegal in many jurisdictions.

DeDECTive: The DECT Toolkit