Category: Security

Backtrail Pro: An Open-Source App for Discontinued goTenna Mesh Radios and Meshtastic

Thank you to Patrick Gartner for writing in and sharing Backtrail Pro, a new iOS and Android app that brings discontinued goTenna Mesh radios back into use and also supports Meshtastic. The goTenna Mesh is a pocket-sized 1 W radio for the 902 - 928 MHz ISM band that pairs with a phone over Bluetooth for mesh texting without cell service.

The company behind goTenna Mesh has since shifted focus to military and public safety customers with its goTenna Pro line. In 2024, the security researchers who disclosed a series of goTenna vulnerabilities noted that goTenna discontinued support for the goTenna v1 and Mesh and exited the civilian market, around the same time CISA published its advisories on the Pro line. The consumer app has since disappeared, and goTenna was acquired by defense autonomy company Forterra in October 2025, leaving many owners with working radios and no app. With no vendor support, it's also unlikely that the Mesh's disclosed vulnerabilities, such as spoofed message injection with an SDR, will ever be patched.

Backtrail Pro talks to the goTenna Mesh through an independent implementation of its Bluetooth protocol, building on earlier community reverse engineering work. It supports group and direct messages, delivery receipts, location sharing, and optional AES-256 encryption. For Meshtastic radios, it lists every node heard and can change basic radio settings. The goTenna Mesh uses FSK rather than LoRa, so the two radio types can't talk to each other directly. However, with one of each connected to the phone, an optional relay can re-send group messages between the goTenna group and the Meshtastic mesh. The app costs US$0.99 on the Google Play Store and Apple App Store with no account or servers, and the code is open-source under GPL-3.0 and available on GitHub.
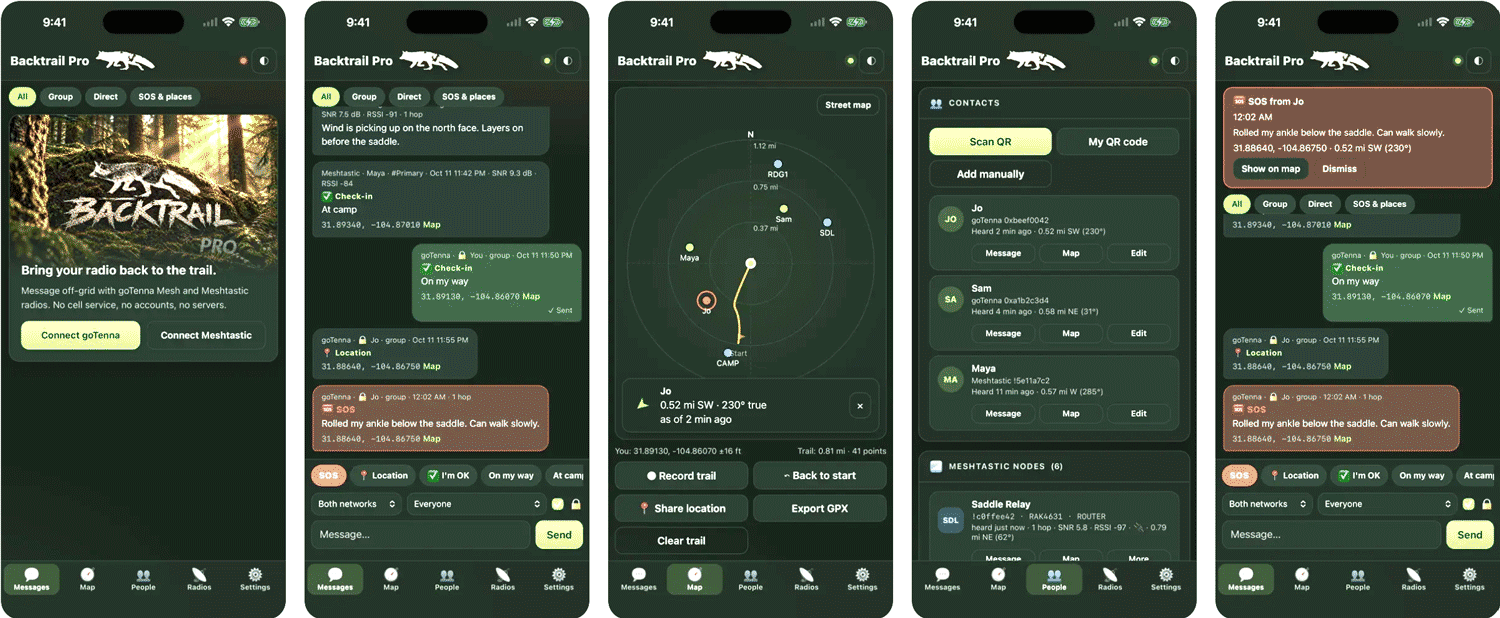
Backtrail Pro App for GoTenna Mesh Radios

AI Disclaimer: The Backtrail commit on GitHub lists Claude as a co-author.
SPECTER: Leaking Data from Air-Gapped Computers by Toggling USB Power States

This October, researchers Hyeongjun Choi, Ji Hyuk Jung and Ji Won Yoon from Korea University and 78ResearchLab in Seoul have published a paper describing "SPECTER", a covert channel that leaks data from air-gapped computers by repeatedly switching the power state of attached USB devices. This first requires installing malware with root or administrator privileges, which then controls power via the operating system's suspend or disable/enable controls. No modification to the peripheral's hardware or firmware is needed.

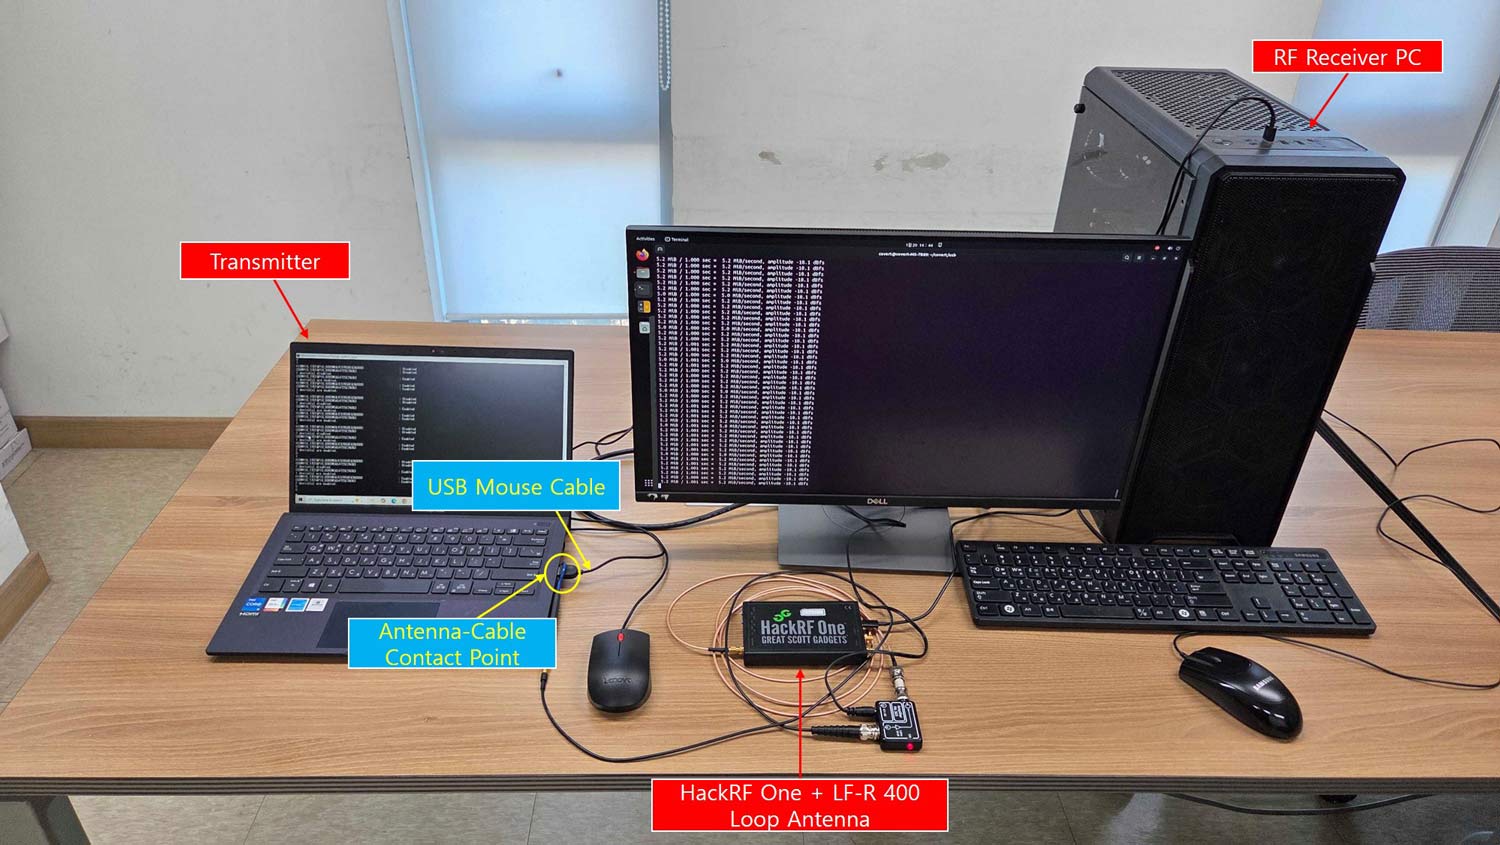
Three receiving methods were demonstrated, with one being RF based. The first method uses a phone plugged into the port, which then simply logs its charging state as on/off binary data. The second method uses a connected mouse, webcam or USB hub whose status LEDs can be watched by a person or camera. The final method uses a HackRF One with a near-field loop probe to pick up the switching emissions at around 5 MHz. Data rates are only 0.2 to 1 bit per second, so the channel is only useful for short secrets like passwords or keys.

We note that so far, the RF method was only tested with the probe touching the USB cable. This project is similar to USBee, which we posted about in 2016, where an unmodified USB device was also turned into a transmitter via malware. The difference is that USBee requires a data transfer USB device like a thumb drive to be connected, whereas SPECTER can use any connected USB device, even those that are charge-only.

SPECTER RF Receiver Setup with a HackRF One and Loop Probe

Live TEA1 Decryption Support Added to an osmo-tetra Fork

Over on GitHub, su4am has published a fork of the well-known osmo-tetra-sq5bpf TETRA decoder that integrates TEA1 cipher support based on CVE-2022-24402. Back in 2023, we first posted about the TETRA TEA1 vulnerability discovery. Midnight Blue, a security research team, discovered this vulnerability as part of their TETRA:BURST research. The discovery found that a key-scheduling flaw reduces the effective keyspace from an impossible-to-brute-force 2^80 down to 2^32, which is small enough to brute force in a few minutes on a commodity GPU. This fork combines the osmo-tetra-sq5bpf TETRA decoder with Midnight Blue’s TETRA_crypto library so that recovered 32-bit keys are applied on the fly to encrypted voice bursts directly inside the decoder.

Importantly, we note that the fork does not crack keys by itself. The tetra-rx decoder outputs “key recovery candidate” tuples from the air, which you then feed into a separate GPU tool (SQ5BPF’s teatime) to actually brute force the reduced keyspace. Recovered keys are added to a keyfile and loaded live, so decryption begins on the next burst without restarting the pipeline. The fork also adds a dual-socket TRA output, letting you monitor decrypted and unencrypted traffic simultaneously with two telive-2 instances. 

We want to warn that intercepting or decrypting communications you are not authorized to receive is illegal in most countries.

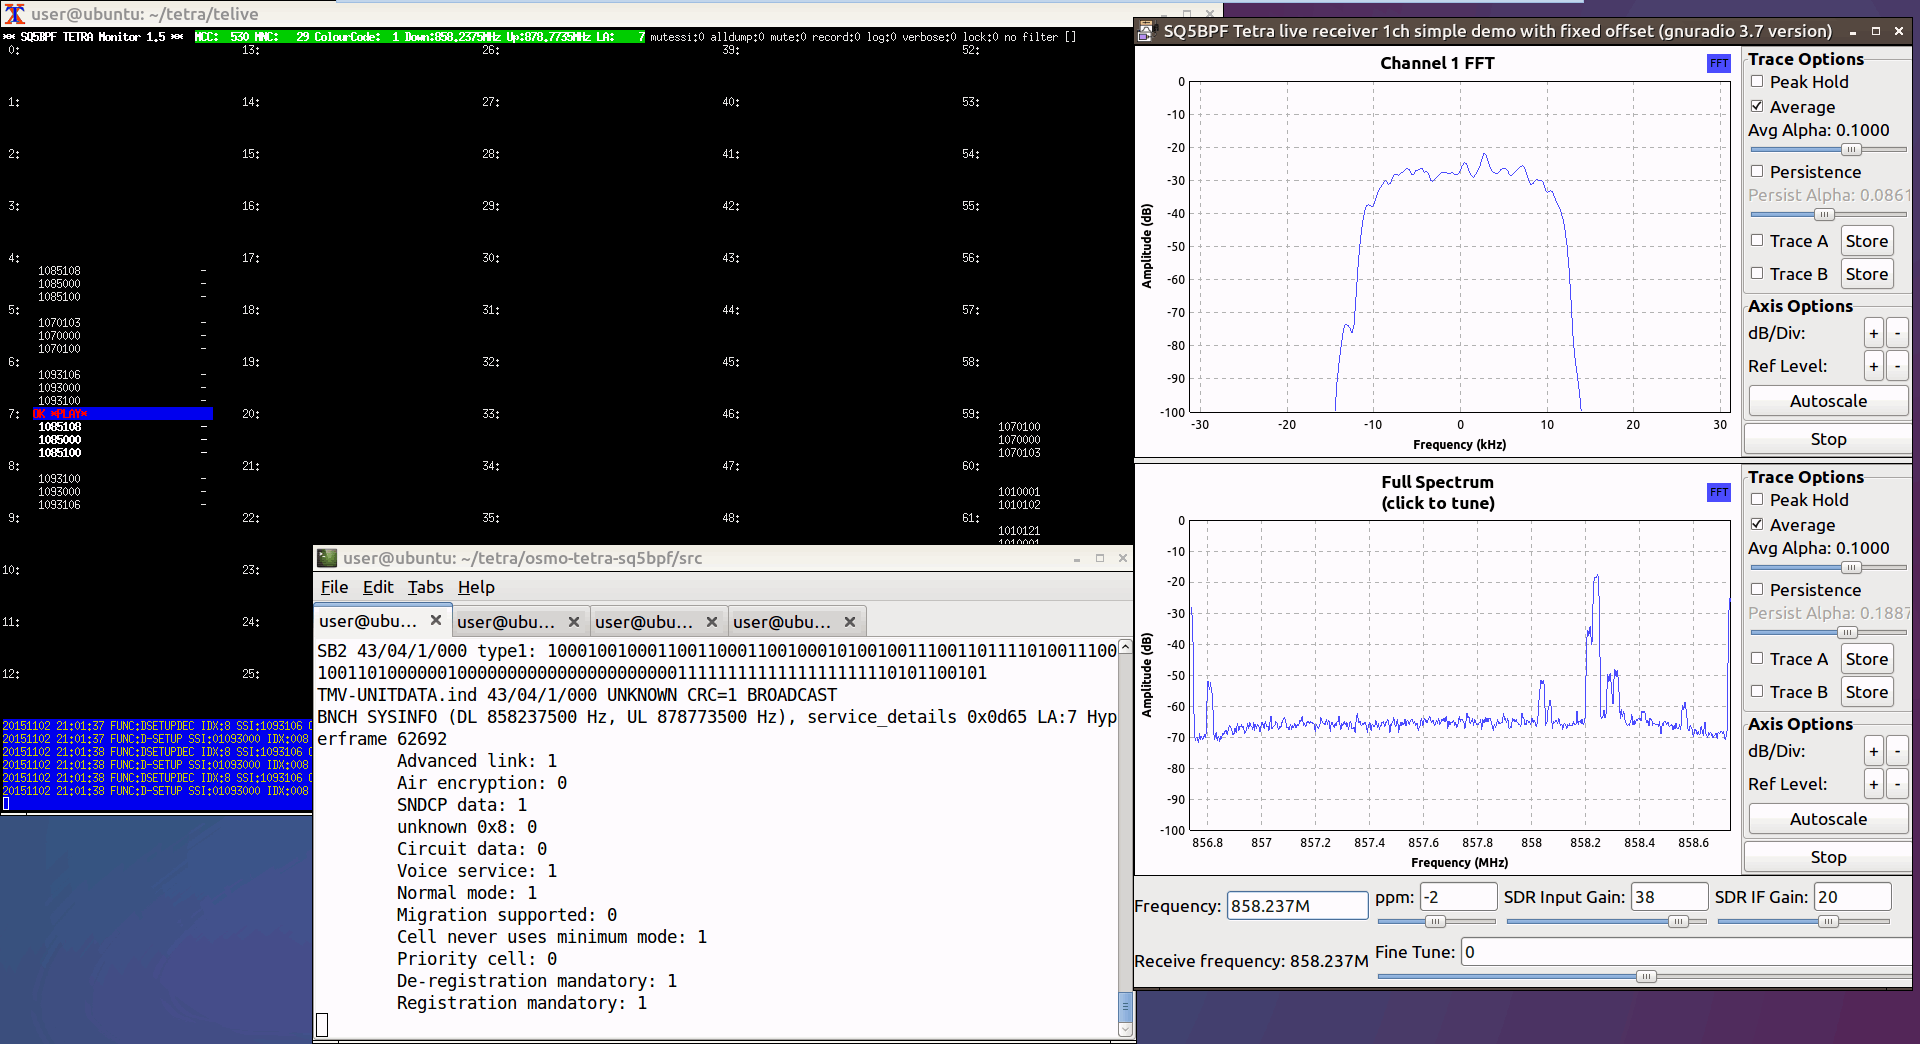
TETRA Decoding (with telive on Linux)

Turning a Smartphone’s Speaker Amplifier into a Silent Intentional VHF Morse Transmitter

Thank you to Efe Işık (TA1EEI) for writing in and sharing with us his open-source project showing how to turn a modern Android smartphone’s internal Class-D speaker amplifier into a silent, intentional VHF Morse transmitter. Efe writes:

By pushing inaudible 21 kHz full-amplitude PCM audio via Android's AudioTrack, the amplifier's PWM switching circuit radiates near-field RF harmonics into the 144 MHz (VHF) band. The signal is strong enough to be received in AM mode on common SDRs and BK4819-based handheld transceivers (such as the Quansheng UV-K5) simply by placing the antenna near the speaker grill.

Everything is open-source, requires zero Android permissions, and includes instructions on receiver setup and frequency alignment.

With the software running on the Android device, simply use an SDR or handheld radio to look for the signal in the 144 - 146 MHz region. Increasing the volume can help increase transmission power.

This reminds us of the TrojPix project, a more sophisticated method that uses a program on a PC to imperceptibly modulate pixels on a screen, effectively turning video cable/screen EMI into an air-gapped data transfer path.

InjectEave: Eavesdropping on Headphones by Injecting a Carrier and Listening to the Modulated Retransmission

Researchers from the Hong Kong University of Science and Technology (Guangzhou) and the Hong Kong Polytechnic University recently published a paper titled "Injected and Leaked: Actively Inducing Side-Channel Leakage Using Electromagnetic Injection and Hardware Nonlinearity".

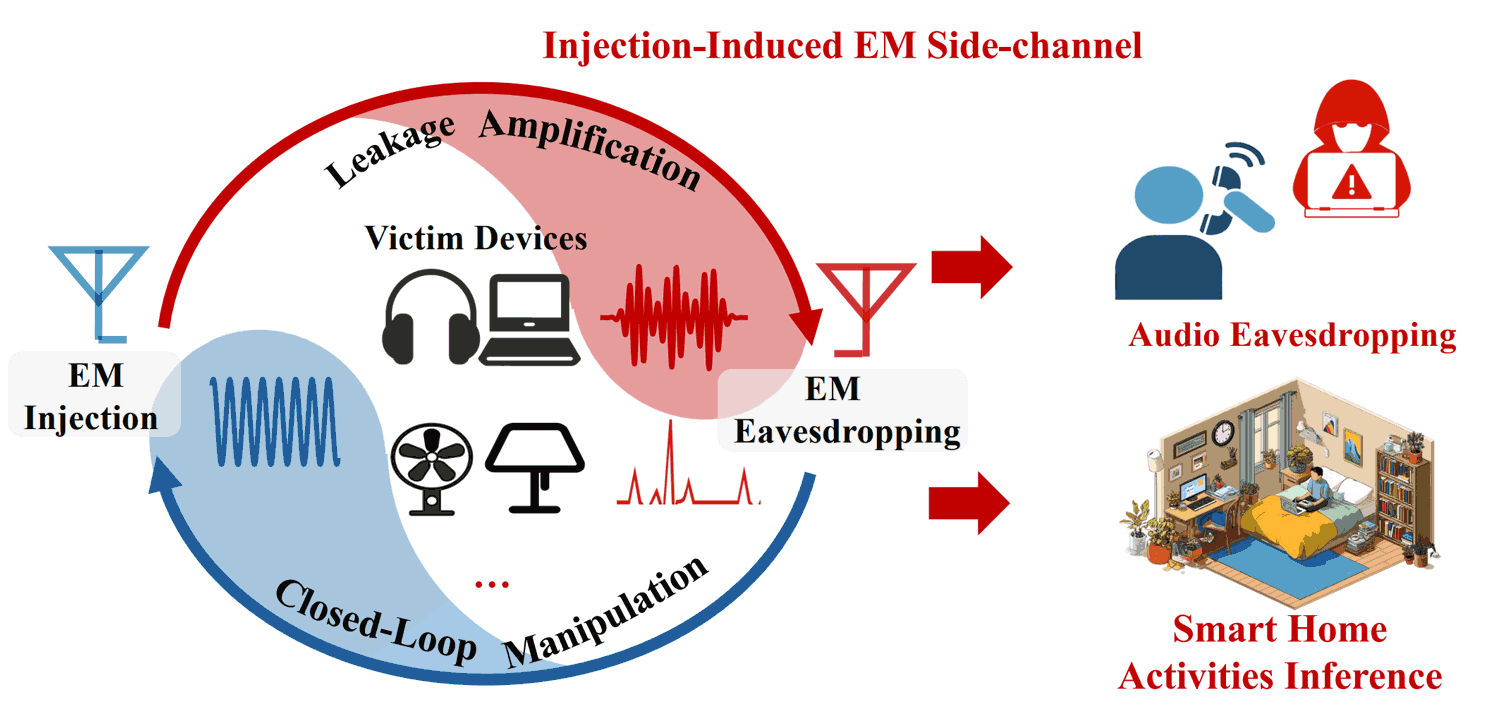
The paper describes how an attacker can use a directional antenna to transmit a carrier signal toward an electronic device, where nonlinearities in its components modulate the signal, which connected cables then re-radiate as unintentional antennas. The attacker can then receive the modulated carrier at the same frequency as it is transmitted and demodulate the modulated sidebands.

The Injecteave Process

In their experiments, they used a USRP B210 software-defined radio to transmit the CW injection signal at anywhere from 0 to 8 MHz (the exact frequency for a device is not specified in the paper for ethical considerations), and a spectrum analyzer to receive the injection-induced EM leakage. The spectrum analyzer demodulates the received mixed signal, then routes the baseband to a PC for further processing. They show how various wired and wireless headphones exhibited injection-induced leakage via the amplifier, and how landline desk phones, smart fans, and lamps were also susceptible.

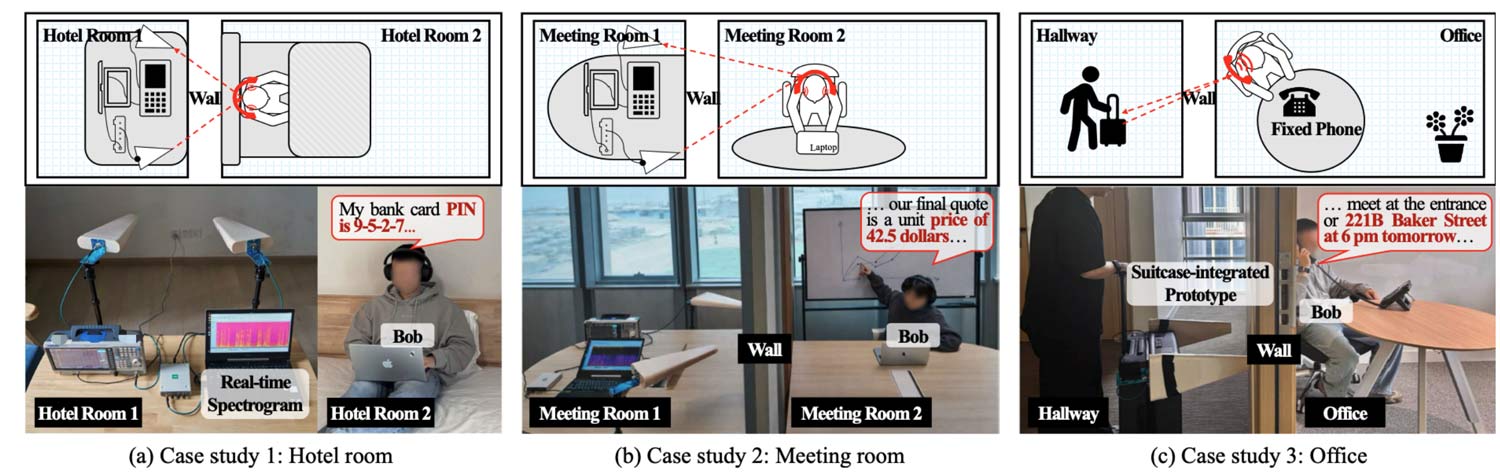
They also show a real-world application where they eavesdropped on audio from headphones and desk phones through walls in a hotel, meeting room, and office.

Update: Thanks to a commenter for pointing out the InjectEave demo page at https://injecteave.github.io.

InjectEave: Real World Examples

An HTML Browser Page that Uses Display Pixel Clock EMI Leakage to Transmit VHF Morse Code

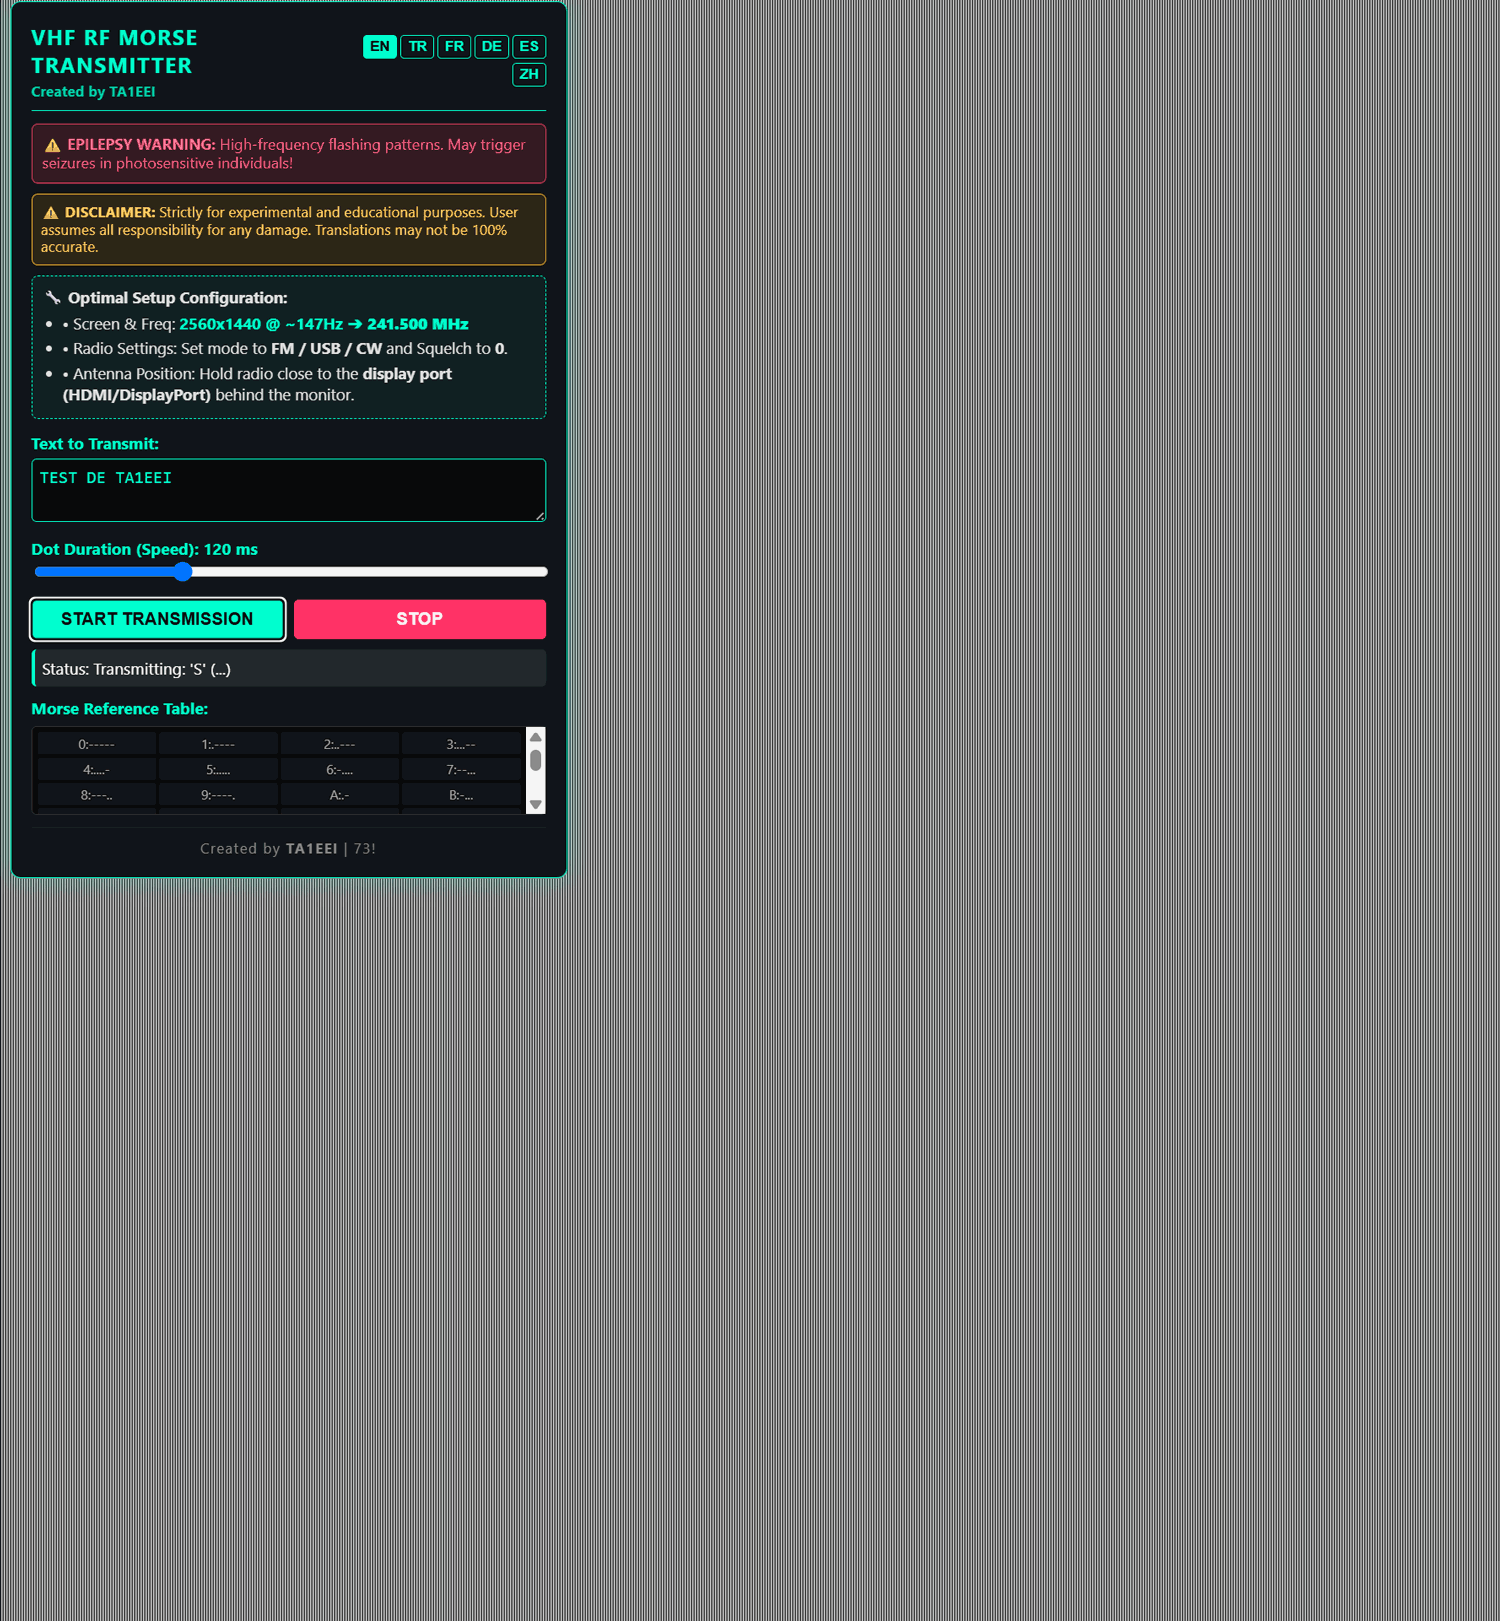
Thank you to Efe (TA1EEI) for writing in and sharing an HTML web tool he created that uses a PC monitor to transmit Morse code. The tool works by modulating the monitor's pixel clocks to intentionally generate EMI leakage in the form of a Morse code signal. It transmits at 148.5 MHz.

Efe's work appears to be a much simpler version of TrojPix, a University research project that we posted about back in July. TrojPix is a more advanced system that introduces imperceptible pixel modulations into the screen, making high-bandwidth wireless data transfer possible via monitor EMI leakage.

The GitHub project page for Efe's VHF Monitor RF Transmitter explains exactly how the project works, including the video pixel clock and how it can be modulated and transmitted wirelessly. Efe has also provided a link to a Reddit post where there is a video, and discussion. 

VHF Morse Code Transmitted via an HTML Page

More Information about the FrameRF Technical Surveillance Counter-Measures Platform – Technical Guest Post

Earlier this month, we posted about Stefano Cangiano, an Italian TSCM (Technical Surveillance Counter-Measures) specialist, and his recently released FrameRF product. Stefano describes FrameRF as "a professional SDR-based TSCM analysis platform designed to help operators rapidly identify, classify, and prioritize RF signals in complex environments." Its main use case is for identifying RF bugs, corporate security audits, and finding anomalous signals.

Recently, Stefano wrote in again and wanted to share some further technical details about his product. Stefano notes that the core idea of FrameRF is to solve the TSCM question: "What happened in the RF environment over the last few hours, and how did it behave?" The system logs RF activity as timestamped events across cellular, Wi-Fi, BLE, DECT, and other signals, correlates them with physical events, and highlights anomalies and intermittent transmitters like event-triggered GPS trackers as leads for further investigation.

Stefano's full write-up is available as a PDF, which you can download here.

The FrameRF Product
The FrameRF Product

KrakenSDR Tested as a GNSS Jammer and Spoofer Localizer

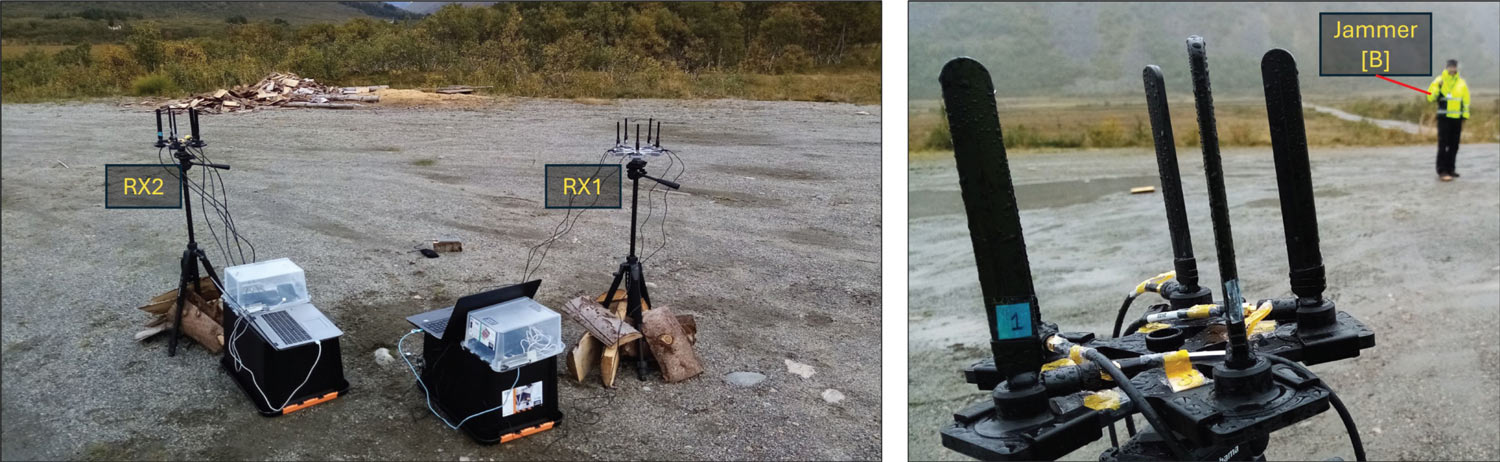
KrakenSDR is our 5-channel coherent software-defined radio designed for applications such as radio direction finding. It was successfully crowdfunded on Crowdsupply back in 2021. We've recently come across a 2025 paper in the Journal of the Institute of Navigation, describing how KrakenSDR was successfully tested as a real-world GNSS jammer and spoofer localizer.

Global Navigation Satellite System (GNSS) services such as GPS are easily jammed by hostile terrestrial signals due to their low transmit power. Jamming is commonly used in modern conflict environments, and is seen heavily in use around Ukraine, Russia, and the Middle East. Similarly, spoofing, which is transmitting a fake GNSS signal to trick receivers into seeing fake locations, is also in use. 

In their paper, Lasse Lehmann et al. from the Technical University of Denmark demonstrate the use of a KrakenSDR for detecting GPS L1 jammers at 1575.42 MHz. The tests were performed at Jammertest 2023, an annual event for open GNSS experiments, and they were able to locate a spoofer down to 18.1 meters via a vehicle-mounted KrakenSDR .

A KrakenSDR Setup at Jammertest 2023