Thank you to Wu Jun (aka jjjwu on GitHub) for writing in and sharing a guide to capturing Wi-Fi channel state information (CSI) from a GL.iNet GL-MT6000 router, along with the 'Router CSI Toolkit' scripts that go with it. CSI is the per-subcarrier amplitude and phase data that a Wi-Fi receiver measures to equalize the channel. Because it changes as people move through a room, it is often used for experimental Wi-Fi sensing.
The router is based on the MediaTek MT7986 chipset and runs OpenWrt with an existing mt76 driver CSI patch from the ossiemarks OpenWrt fork. A small daemon on the router streams 80 MHz, 256-subcarrier CSI from the 5 GHz radio over UDP to a host PC. There, Python scripts check the capture quality and produce amplitude heatmaps and a simple motion metric. A 10-minute test run produced 57,293 per-chain records at about 95.5 records/s.
While this project doesn't use an SDR, it may interest readers who followed BirriaSDR and Mtk79ICAP, which also patch the mt76 driver to turn MT7921 Wi-Fi dongles into SDRs. The scripts are MIT-licensed and available on GitHub, and the 10-minute dataset is on Zenodo under CC BY 4.0.
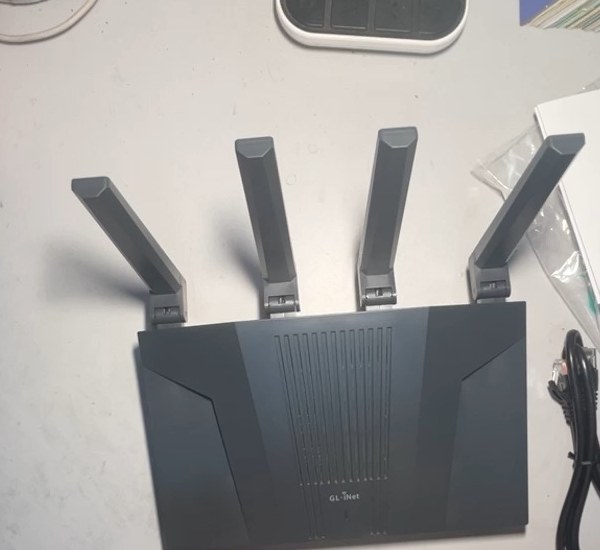
The GL-MT6000 (MT7986) Router used in these experiments
Last week we posted about BirriaSDR, which turns cheap MT7921-based USB 3.0 Wi-Fi dongles into a 2.4 / 5 GHz SDR. Now Daniel has written in about his project Mtk79ICAP, a similar project that uses a forked Linux mt76 driver and a patched MediaTek firmware to stream 14-bit I/Q from the chip’s internal capture engine.
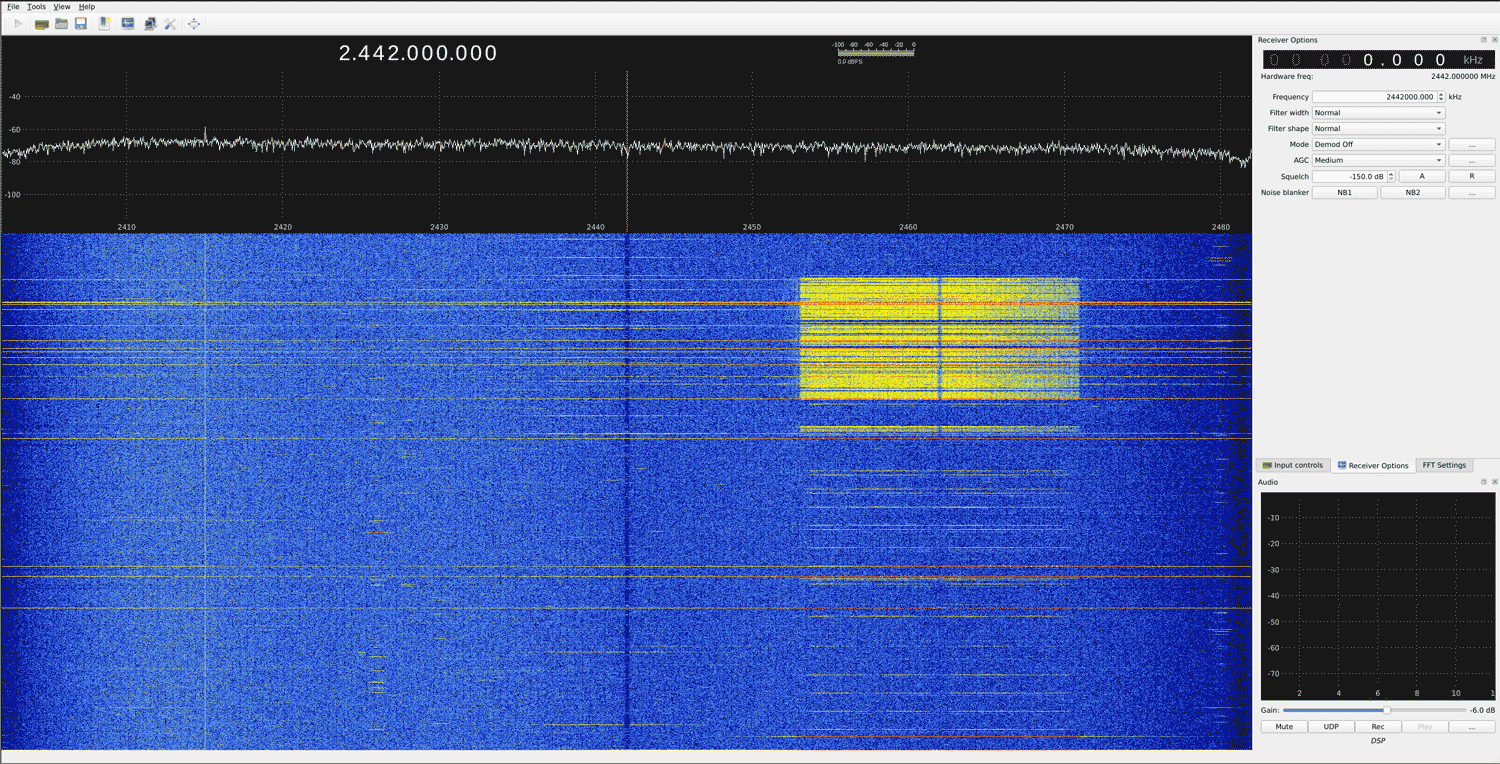
The key difference is that Mtk79ICAP includes a SoapySDR module, so the dongle works directly in GQRX, SDR++, and GNU Radio Companion. It supports 20, 40, and 80 MHz bandwidths on both bands, including 80 MHz on 2.4 GHz, and Wi-Fi monitor mode can keep running in parallel while I/Q is streamed.
The project is still experimental and Linux-only, with uncalibrated levels and some variability at 80 MHz on 2.4 GHz. Still, with multiple teams now working on these dongles, the MT7921 is quickly maturing into a usable, low-cost wideband SDR.
With AI-in-the-loop reverse engineering, things are heating up, and we're starting to see a gold rush of reverse-engineered Wi-Fi radios turning into software-defined radios. Just yesterday, we posted about h0m3us3r's discovery of how a Gemtek W1700K Wi-Fi 7 router could be turned into a 320 Msps SDR. And the week before, we posted about the ESP32-SDR discovery.
Today, a new Wi-Fi dongle-turned-SDR has been discovered, and this time it is probably the most accessible one. Over on X @luigifcruz, author of the popular CyberEther tool, has announced that he has reverse engineered a commodity US$30 USB 3.0 Wi-Fi dongle with the help of GPT-6 Astra, and discovered a RAW I/Q stream which can be exported over USB3.0. This effectively turns the Wi-Fi dongle into a 2.4 GHz / 5 GHz SDR, capable of exporting 40 Msps at 14-bit ADC resolution. Luigi named the new SDR 'BirriaSDR' after the Birria Taco he was eating at a restaurant while using AI to reverse-engineer the WiFi dongle. The open-source repo is available on GitHub.
This is probably the most accessible of the newly discovered Wi-Fi SDRs because it is cheap, mass-produced, readily available, and has useful export bandwidth. The ESP32-SDR suffers from a lack of usable export bandwidth, meaning that getting usable amounts of IQ data onto a PC is impossible without hacking in an FPGA. The Gemtek W1700K Wi-Fi 7 router has an incredible 320Msps IQ bandwidth and an effective export via Ethernet, but it is expensive and not really available for purchase anywhere anymore.
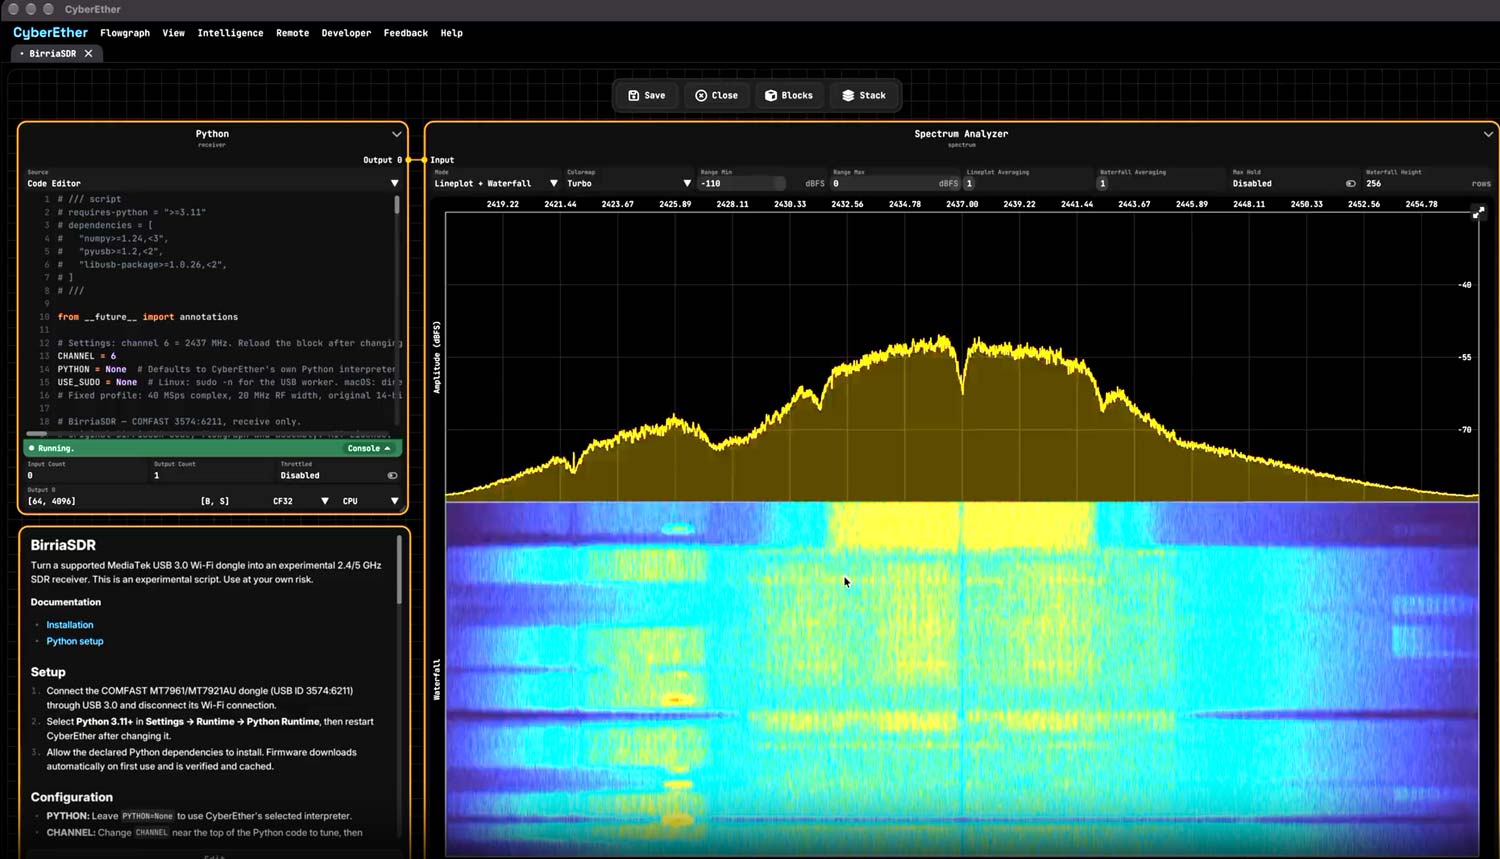
Luigi has added support for the BirriaSDR in his CyberEther software through an input block and sample flowgraph.
It remains to be seen how popular these dongles will become, and if they'll become a new type of RTL-SDR like device. If there is a sudden influx of purchasers, sellers may put the pricing up. We also note that Wi-Fi dongles are limited to the 2.4/5 GHz bands, where there aren't that many interesting signals to play with. However, as Luigi suggests, modifying the dongle to add a front-end mixer is a possibility. The HackRF already uses a 2.4 GHz IF architecture, so a similar type of front end could be used.