Category: Security

Receiving Analog TV from Turkmenistan Unintentionally Bouncing off a Russian Military Satellite

Over on Twitter @dereksgc has been monitoring the 'Meridian' communications satellites, which are Russian owned and used for civilian and military purposes. The satellites are simple unsecure repeaters, meaning that actually anyone with the hardware can transmit to them, and have their signal automatically rebroadcast over a wide area. This has been taken advantage of recently by anti-Russian invasion war activists who have been trolling the satellite with SSTV images of the Ukrainian flag, as well as audio.  

Apart from intentional abuse, a side effect of being an open repeater is that sometimes the satellite can pick up powerful terrestrial signals unintentionally, such as analogue broadcast TV from Turkmenistan. Over on his blog, @dereksgc has written up an excellent post documenting the background behind this finding, his entire setup involving the hardware he's using and how he's aligning with the satellite, and what software he is using to decode the TV signal. In his hardware setup he notes that he uses a HackRF, but that a RTL-SDR would suffice.

New York Times Story on Intercepted Russian Forces Radio Communications

The New York Times have recently run an incredible video story about how Russian radio communications are being intercepted and recorded by ham radio operators and open source radio monitoring hobbyists in Ukraine. Some of the communications reveal the extent of the logistical issues experienced by the invading forces, and perhaps have even recorded evidence for war crimes.

It appears that much of the invading Russian forces use simple unencrypted analogue voice over HF channels that can be intercepted and recorded by anyone with an HF software defined radio, or anyone willing to monitor nearby web-based SDRs like KiwiSDRs and WebSDRs. In the video screenshots of recordings played back in SDR# and various WebSDRs are displayed.

The story focuses mostly on the audio recordings that highlight communications between Russian forces discussing attack plans, including plans to bombard residential areas with artillery. These recordings are cross-referenced with reports and videos of actual tank sightings and destruction in the areas discussed on the radio.

A later recording highlights communications from a distressed Russian vehicle under attack, requests for air support being unfulfilled, and urgent requests for supplies like fuel, food and water. 

Russia Struggled to Capture a Ukrainian Town. Intercepted Radio Messages Show Why.

Some of the monitoring projects involved are highlighted in the story and they include, Project Owl, Ukrainian Radio Watchers, ShadowBreak and NSRIC (Number Stations Research and Information Center). We are also aware of at least one other organization attempting to record communications within Ukraine as well that may be making use of RTL-SDRs, HackRFs and other SDRs.

Mapping GPS/GNSS Interference Through ADS-B Data

Websites like adsbexchange.com log ADS-B aircraft tracking data from contributors located all over the world and aggregate it all onto a single map. Typically an RTL-SDR is the receiver of choice for contributors receiving ADS-B signals. One piece of data that is recorded with each packet is GPS/GNSS accuracy.

Over on Twitter John Wiseman @lemonodor has been using the aggregated ADS-B data provided by adsbexchange to highlight regions where ADS-B GPS inaccuracies are significant. This may allow us to use crowd sourced data to detect regions of GPS interference or jamming. In one of his latest findings he noted extreme GPS inaccuracy that noticed around the Baltic regions (Poland, Lithuania, Latvia, Kaliningrad).

As John and others reported in subsequent Tweets, this GPS interference was noticed by others too, with some flights needing to be cancelled or needing to return during their journey, and a NOTAM warning being issued to pilots regarding the interference. Reuters also reported on the GPS disturbance a few days later.

NOTAM: GPS INTERFERENCE DETECTED IN THE EASTERN PARTS OF HELSINKI FIR. AFFECTED AREA SECTOR N, SFC-FL200

It is well known that Russia routinely utilizes GPS spoofing or jamming around Kremlin landmarks, sensitive areas and during military operations. However, others noted that NATO exercises in the Baltic could also be the cause.

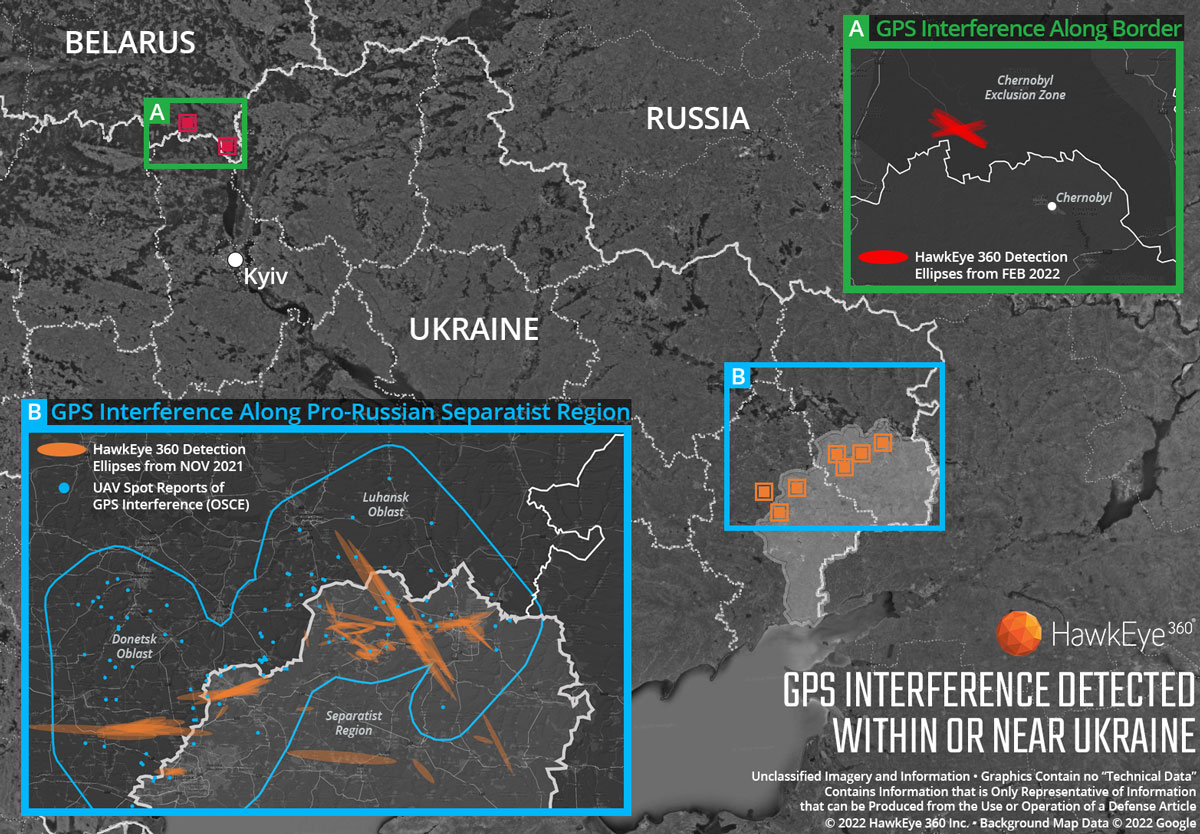
To further add to this story, the satellite intelligence operator Hawkeye 360 also recently detected significant GPS interference within or around Ukraine.

Hawkeye360 Detects GPS Interference near or within Ukraine.

Samy Kamkar Talks Hardware Security on Hackster Café

Samy Kamkar is famous in the wireless and hardware information security scene for his research on various security exploits including methods to defeat rolling code security, and using a children's toy to open wireless garage doors. In a recent Hackster.io Hackster Café interview Samy talks about various security related topics including software defined radios.

Samy Kamkar first became notorious for software and hardware security exploits – including SkyJack, a custom drone that could take control of other UAVs, and OpenSesame, a hacked child's toy that can open remote-controlled garage doors. He now brings this deep experience to Openpath, the touchless access control company he co-founded in 2016. From security celebrity to founder, we sit down for a chat with Samy on this episode of Hackster Café (new episodes every Tuesday at 10am Pacific).

Samy Kamkar on Hardware Security // Hackster Café

A Warning to Ukraine Based RTL-SDR Hobbyists

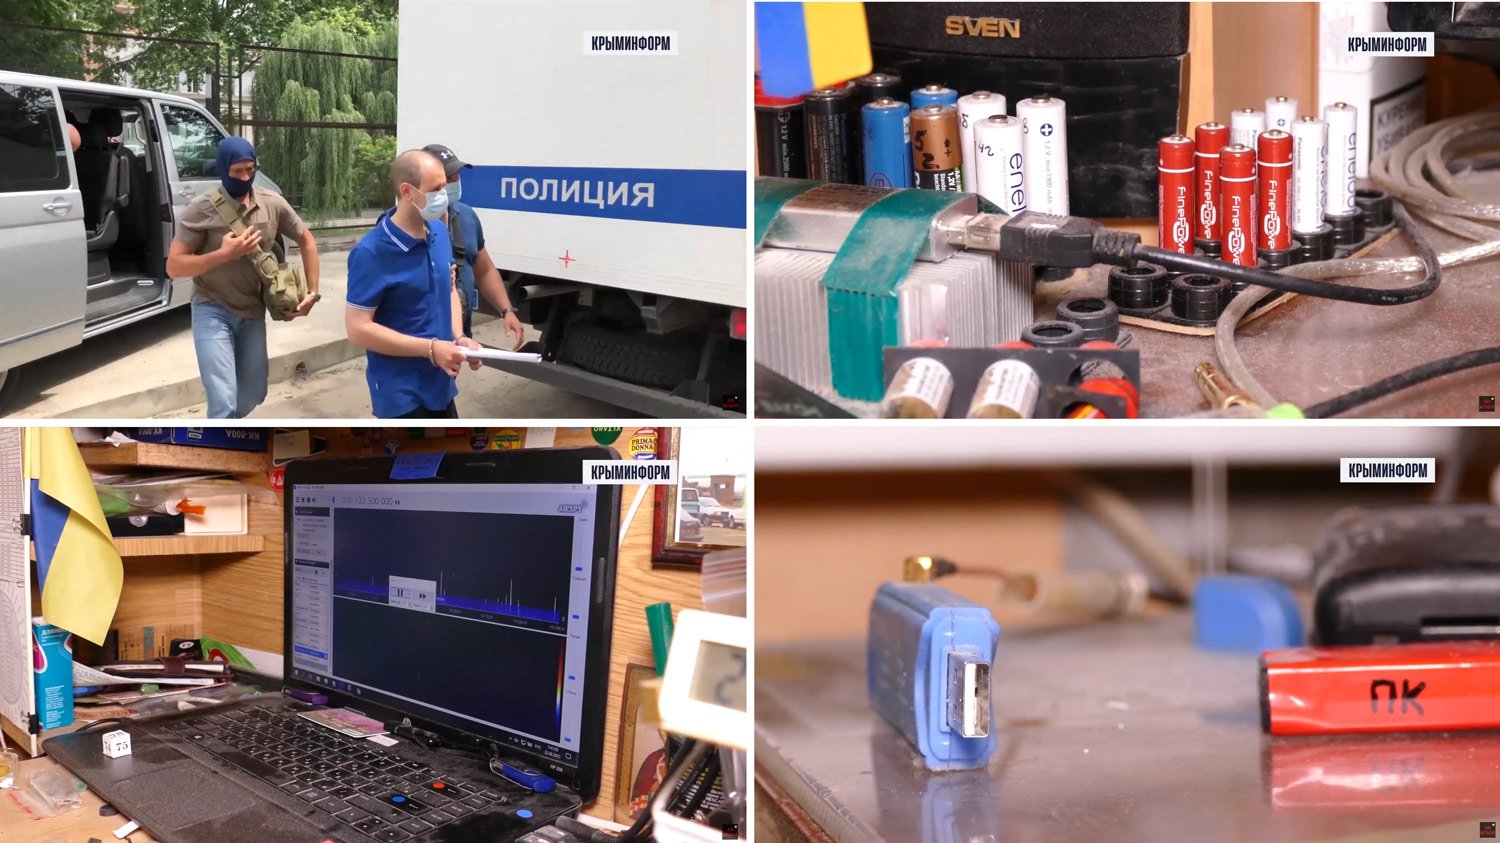
While we usually don't encourage politics on this blog, with the possibility of a Ukraine invasion by Russia we just wanted to issue a general warning to Ukrainian SDR owners. Last year we saw Stanislav Stetsenko a resident of Crimea arrested by the Russian Federal Security Service under suspicion of being a Ukrainian informant. The evidence against him was that he was an aviation and plane spotter hobbyist who used RTL-SDRs for listening in to aircraft communications - something of which many of us do in safety. 

Back in June 2021 Stanislav was facing 25 years in prison. We still don't know what has happened to him. If anyone local has heard any updates please let us know. (UPDATE: US1GBF in the comments below knew Stanislav personally and has provided an update: Stanislav was reportedly transferred from Crimea to a Moscow prison. The Ukrainian authorities are working on the exchange of Stanislav. However, the exchange has already been postponed many times because of the refusal of the Russians to diplomacy. Work continues.)

From our website and sales statistics we know that there is a sizable RTL-SDR community in the Ukraine. We don't know what will happen if there is an invasion, but it's possible that, like in Crimea, Russian security forces will see SDR hobbyist activities as a threat, so we urge Ukrainian residents to have a plan to take down any web feeds and antennas should it come to the worst.

EDIT: This post has stirred up quite the discussion. As long as comments remain civil comments will remain open. This post is not intended to take sides. Whilst many Ukrainians in the amateur radio community already know to keep their activities safe during conflicts, we are aware of many young Ukrainian STEM students and hobbyists that may be somewhat insulated or not care about geopolitical events, who read our blog and copy activities that are safe to perform in most countries, but may not be safe in the Ukraine during times of conflict.  

Crimean resident arrested for RTL-SDR use in June 2021

Reverse Engineering a 30 Year Old Wireless Garage Door Opener with a HackRF and GNU Radio

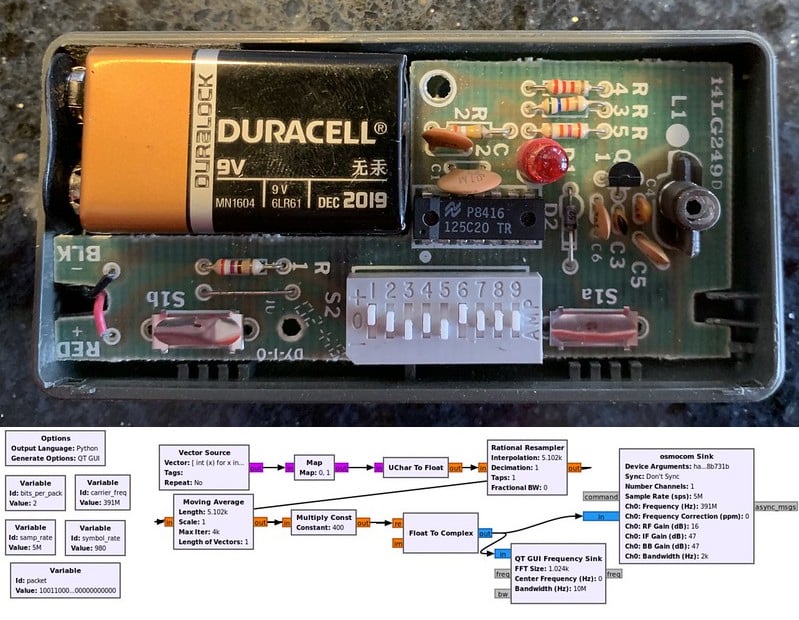
At his childhood home Maxwell Dulin discovered that his garage door was controlled by a 30 year old system called the "Sears Craftsman 139.53708 Garage Door Remote". Being interested in SDRs Maxwell decided to see if he could reverse engineer the remote using his HackRF.

His first steps were to search for the frequency which he found active at 390 MHz. He then moved on to analyzing the signal with Inspectrum, discovering the OOK modulation, then working his way towards the binary control strings. One thing that helped with his reverse engineering was the use of the 9-bit DIP switches on the remote that configure the security code that opens up a specific door as this allowed him to control the transmitted bits, and determine which bits were used for the security code. With this and a bit of GNU Radio code he was able to recreate the signal and transmit it with his HackRF.

Finally Maxwell wanted to see how vulnerable this door is to a brute force attack that simply transmits every possible security code. Through some calculations, he discovered that brute forcing every possible security code in the 9-bit search space would only take 104 minutes to open any garage using this opener.

GNU Radio replaces a 30 year old garage door remote

Remoticon 2021: Smart Meter Hacking Talk

Remoticon 2021 was an online conference held in November 2021 and videos of presentations have recently been uploaded to the Hackaday YouTube channel this month. One very interesting talk was the presentation by Hash Salehi (RECESSIM) on reverse engineering electricity smart meters that are used to remotely monitor and bill home electricity usage in some neighborhoods.

In the past we've posted about Hash (RECESSIM)'s series on smart meter hacking a few times before. In this latest talk Hash summarizes his smart meter hacking experience, talking about how he went from reverse engineering the firmware, to using an SDR to capture and decode information from all the smart meters in his neighborhood, and finally to determining how to actually transmit data to his own smart meter network.

Hackaday have also posted a full writeup on his talk. This is a very in depth reverse engineering project so it is a great talk to learn from.

Remoticon 2021 // Hash Salehi Outsmarts His Smart Meter

Snooping Network Traffic from LAN Cables with an RTL-SDR or HackRF

Mordechai Guri is a cyber-security security researcher at Israel's Ben Gurion University of the Negev. Recently Guri has described a method for sniffing network data from LAN Ethernet cables over an air gap through the use of RTL-SDR or HackRF software defined radios. Guri's paper is available directly here.

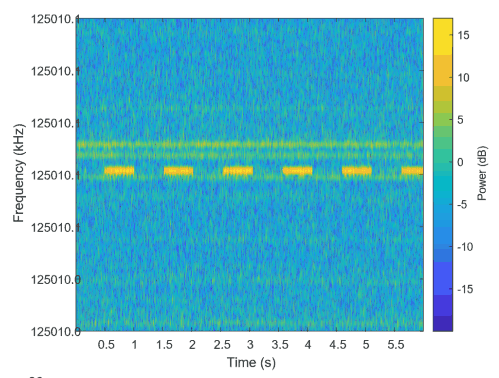
The idea behind the attack is that ethernet cables can act as an antenna, leaking signals at frequencies which can easily be sniffed by a SDR. The specific technique in the paper does not decode normal network traffic, instead it requires that malicious code which modulates a custom signal over the ethernet cable be installed on the PC first. The technique used appears to be similar to what the Etherify software by SQ5BPF uses, which modulates data in morse code by turning the network card on and off.

Receiving a signal modulated by the LanTenna malware