Category: Security

Receiving SSTV from FleetSatcom Pirates

Radio pirates often make use of the Fleetsatcom satellites to send and receive slow scan television (SSTV) pictures over a wide distance. Fleetsatcom is a satellite communications system used by the US Navy for radio communications. Since these satellites are simply radio repeaters with no authentication mechanisms, pirates soon discovered that they could take over the satellites for their own use.

Over on YouTube user LEGION ELMELENAS has uploaded a video showing his reception of some pirates transmitting a SSTV image at a Fleetsatcom frequency of 252 MHz. To receive the image he used a home made turnstile antenna, an RTL-SDR dongle, SDR# and the RX-SSTV decoder. The image appears to be a photo of a pirates son.

We previously posted more information about Fleetsatcom SSTV pirates in this post.

SSTV from Satcom satellites. RTL-SDR SDRSharp FLTSATCOM pirates

SDR Capture The Flag Competition Tutorial

During several hacker and security themed conferences (Shmoocon, Bsides, Derbycon, Defcon, etc) organizers from Wireless Village have been setting up competitive WiFi and SDR themed capture the flag (CTF) games. In the competition the organizers broadcast a signal and the competitors are required to complete various tasks (capturing flags) such as determining the centre frequency of the transmission, demodulating the signal and finding any meta data contained within the signal such as codec flags in DVB-T signals and RDS data in FM signals. The team which captures the most flags wins a prize. The process of capturing flags often requires the use of some sort of software defined radio like the RTL-SDR, HackRF or BladeRF.

Recently, Russell one of the CTF organizers wrote in to let us know about a SDR CTF training resource that he has put together. The site contains various exercises/tutorials that allow participants to practice the skills needed to compete in the competition. Most exercises involve using a Raspberry Pi together with PiFM for transmitting a simulated competition signal, then receiving and demodulating the signal with a SDR. The exercises include running rtl_power, setting the PPM offset, decoding morse code, AFSK, RDS, ASK/OOK, DVB-T, POCSAG, MotoTRBO, SSTV and decoding numbers stations.

village-sq

Spying on Keyboard Presses with a Software Defined Radio

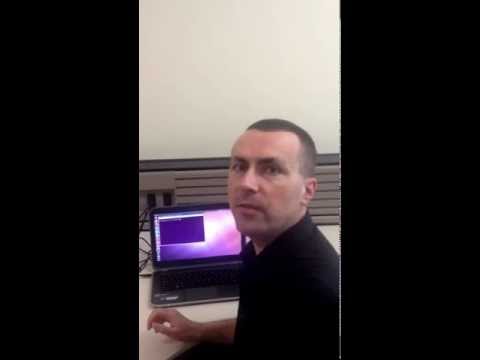
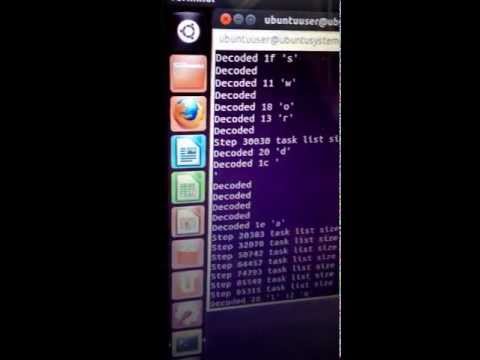
Last year Milos Prvulovic, a computer science researcher uploaded some videos to YouTube showing how he was able to remotely and covertly record the keystrokes of a target laptop in another room wirelessly using just a software defined radio, magnetic loop antenna and some custom software.

The target laptop was first modified with special drivers that cause increased and unique memory and processor activity for each key that is pressed. As computers emit unintentional RF emissions, the modified memory and processor activity causes the target laptop to emit a unique RF signature for each key pressed. Milos used this fact to create a program that can detect the RF emissions from the target laptop, and show the key presses made from the target laptop on the spying PC.

EM Covert Channel Attack Setup and Explanation

EM Covert Channel Attack Through a Wall

EM Covert Channel Attack from Nearby Desk

RTL-SDR Cell Phone IMSI, TMSI and Key Sniffer

Over on YouTube user Kali Gsm has uploaded a video showing off a new software program he has written that allows an RTL-SDR to be used to gather IMSI, TMSI and Key information from a cell phone connected to a PC.

The IMSI (International Mobile Subscriber Identity) is a number that uniquely identifies a cell phone. Because IMSI’s are unique, they can be used to track a cell phone so they are rarely broadcast and instead a TMSI (Temporary Mobile Subscriber Identity) number is used to identify a cell phone instead. The TMSI is changed depending on geographic location or changed by the network randomly. The key is a number that is used to decrypt the GSM data sent to your phone.

Kali Gsm’s software is called rtl_tool_kit and is planned to be released soon on it’s GitHub page. It uses the gr-gsm software to sniff the GSM downlink with an RTL-SDR dongle and also interfaces to a connected mobile phone. The author writes that the following is possible with the software:

  1. You can get imsi tmsi and key of the device connected to your pc.
  2. You can send silent/flash sms
  3. You can connect/match tmsi to a mobile number if target is on the same BTS and in GSM900/2G mode.

Update 25/01/2015: All YouTube videos appear to have been removed – though the uploader reports in the comments that the videos will be back online soon.
Update 29/01/2015: Videos are back online.


Chaos Communications Congress Talks – Iridium Pager Hacking

A few days ago the Chaos Communications Congress (a technology and hacking focused conference) commenced. Among the talks there was one about reverse engineering the Iridium satellite paging system using software defined radio. Iridium satellites provide global communications via special satellite phones, pagers and other transceivers.

In the talk the speaker shows how they used a USRP radio together with a cheap active iridium antenna, a bandpass filter and an LNA to receive the Iridium satellite signals. They also mention that an E4000 RTL-SDR together with an LNA and appropriate home made antenna for frequencies in the ~1.6 GHz region can also be sufficient. Once they were able to receive signals they were then able to reverse engineer the signal and create several pieces of software to decode the pager messages. The code is available on their GitHub at https://github.com/muccc/iridium-toolkit.

Sec, schneider: Iridium Pager Hacking

Digital Ding Dong Ditch – Hacking wireless doorbells with Arduino and RTL-SDR

Over on YouTube user Samy Kamkar has uploaded a video showing how he was able to use an RTL-SDR to copy his friends wireless doorbell signal and prank him by replaying it using an Arduino and 433 MHz transmitter. His video goes through the entire reverse engineering process he used from recording the wireless doorbell signal with the RTL-SDR, to analyzing and understanding the signal and finally to programming the Arduino with the code to replicate the doorbell signal. If you don’t like video explanations, Samy has also done a write up of the same material on his website. 

Digital Ding Dong Ditch Prank - hacking wireless doorbells w/Arduino and RTL-SDR

SDR on TV: Using SDR to Break into Homes with Wireless Alarms

Earlier this year the American TV show Good Morning America featured a segment on software defined radios being used to break into houses with wireless alarm sensors. The story is based on a Defcon 2014 paper “Home Insecurity: No Alarms, False Alarms, and SIGINT” by Logan Lamb. In the TV segment Logan shows how he uses a USRP software defined radio to send a false alarm signal, jam a wireless sensor and finally to record sensor activation data from the alarm system.

Although Logan used a USRP, the same attack could be done with the cheaper HackRF.

SDR HackRf: Home Insecurity: No Alarms, False Alarms, and SIGINT

Analyzing a Car Security Active RFID Token with a HackRF

Some car security systems from around 2001 – 2003 use an embedded RFID tag inside the car key as an added security measure against key copying. Using his HackRF, ChiefTinker was able to analyse and decode the data from an active RFID token used in a car key. He notes that the same analysis could also be performed with an RTL-SDR dongle.

Upon powering the RFID tag with a power supply, ChiefTinker noticed that the tag emitted a short transmission every 5 seconds in the ISM band at 433.920 MHz. On closer inspection he determined that the transmitted data was encoded with a simple AM on-off keying (OOK) scheme. After importing the audio into Audacity and cleaning up the signal a little, he was able to clearly see the OOK square wave showing the transmitted binary data.

Next he analysed the data and compared the binary output against two different RFID keys. From the comparison he was able to determine that the tag simply beacons a unique serial number, which is susceptible to capture and replay attacks. After further processing he was able to convert the transmitted binary serial number into hexadecimal, then ASCII to find the unique serial number being broadcast in decimal.

RFID Car Key Tokens
RFID Car Key Tokens